An AI management system (AIMS) is the set of policies, processes, roles and controls an organisation uses to govern how it develops, provides or uses AI systems. ISO/IEC 42001:2023 sets the requirements for one, covering AI risk, AI system impact assessment, objectives, monitoring and continual improvement, and applies to organisations of any size, type or nature.
What does an AI management system include under ISO/IEC 42001?
ISO/IEC 42001:2023 is the international standard for AI Management Systems (AIMS). It sets out what an organisation must do to establish, implement, maintain and continually improve an AIMS, and gives guidance on how to do it. For a wider introduction to the standard itself, see our ISO 42001 overview.
Who does ISO/IEC 42001 apply to?
The standard applies to any organisation that provides or uses products or services that rely on AI systems, whatever its size, type or nature. Under clause 4.1, the organisation decides its role for each AI system, for example as an AI provider, an AI producer or an AI customer, because the role shapes which risks and controls apply.
How does an AIMS map to clauses 4 to 10?
The requirements sit in clauses 4 to 10. The table shows what each clause adds to an AIMS.
| Clause | What it adds to the AIMS |
|---|---|
| 4 Context of the organisation | Internal and external issues, the organisation’s role for each AI system, interested parties and the scope of the AIMS (4.1 to 4.4) |
| 5 Leadership | Top management commitment, an AI policy (5.2) and assigned roles, responsibilities and authorities (5.3) |
| 6 Planning | AI risk assessment (6.1.2), AI risk treatment and a statement of applicability (6.1.3), AI system impact assessment (6.1.4), AI objectives (6.2) and planning of changes (6.3) |
| 7 Support | Resources, competence, awareness, communication and documented information (7.1 to 7.5) |
| 8 Operation | Operational planning and control (8.1), and carrying out AI risk assessment, risk treatment and impact assessment in practice (8.2 to 8.4) |
| 9 Performance evaluation | Monitoring and measurement (9.1), internal audit (9.2) and management review (9.3) |
| 10 Improvement | Continual improvement (10.1) and nonconformity and corrective action (10.2) |
What are the core components of an AIMS?
In practice, most AIMS are built from three core components:
- Ethical principles: Commitments, set out in the AI policy, on how AI systems are developed and used, such as fairness, transparency and privacy.
- Governance structures: Named roles and responsibilities for AI, plus a way for people to report concerns (Annex A controls A.3.2 and A.3.3).
- Risk management processes: Repeatable steps for identifying, assessing and treating AI risks, and for assessing impacts on people and society.
Facilitating Continuous Improvement in AI Systems
Clause 10 of ISO/IEC 42001 asks the organisation to keep improving how suitable, adequate and effective its AIMS is. Monitoring results, internal audits and management reviews feed back into the AI policy, objectives and controls, so AI systems stay aligned with organisational objectives as risks and opportunities change.
An AIMS gives this cycle a consistent structure, so improvements are planned, recorded and checked rather than made one system at a time.
Book a demoWhat ethical principles does an AI management system build in?
Ethical principles form the backbone of an AIMS compliance framework. Annex C of ISO/IEC 42001 lists accountability, fairness, privacy, and transparency and explainability among the potential AI objectives an organisation can adopt.
Which ethical guidelines matter most for an AIMS?
- Fairness: Making sure AI systems do not create or amplify unfair bias against people or groups.
- Accountability: Setting clear lines of responsibility for AI system outcomes.
- Transparency: Making the workings of AI systems understandable to the people affected by them.
- Privacy: Protecting personal and sensitive data that AI systems process.
These guidelines are practical needs, not theory: they are how an organisation earns trust in the AI systems it builds or uses.
How can people challenge or report problems with an AI system?
Accountability means decisions made with AI can be traced back to the organisation and the people responsible. ISO/IEC 42001 supports this in two ways: control A.3.3 asks for a process for reporting concerns about AI systems, and control A.8.3 asks the organisation to give interested parties a way to report adverse impacts of an AI system. Together they give affected people a route to question AI outcomes.
How is responsible AI use achieved?
Responsible AI use under an AIMS is achieved through:
- Risk assessments that identify potential ethical pitfalls.
- Ongoing monitoring to check AI systems operate as intended.
- Engagement with stakeholders to understand and address ethical concerns.
How do you put AI principles into practice?
To put AI principles into practice, organisations should:
- Write clear policies that state ethical commitments.
- Train employees on why ethical AI use matters and how to achieve it.
- Use tools and frameworks that support ethical decision-making in AI development and deployment.
How does an AI management system manage AI risk?
An AIMS manages AI risk through three linked processes in clause 6: AI risk assessment (6.1.2), AI risk treatment (6.1.3) and AI system impact assessment (6.1.4). Clause 8 then asks the organisation to repeat the risk and impact assessments at set intervals, and again whenever a significant change is planned or happens.
How does the plan-do-check-act cycle apply to AI risk?
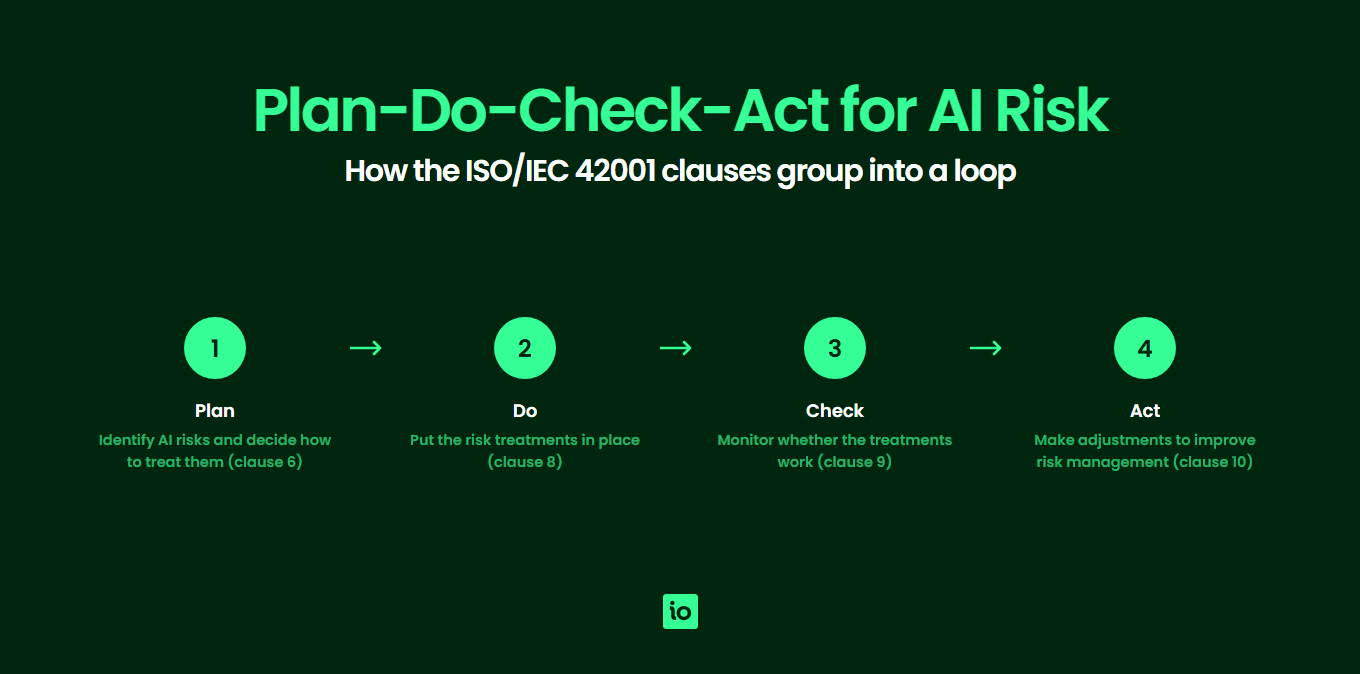
The Plan-Do-Check-Act (PDCA) cycle is a common way to run continual improvement, and the clauses of ISO/IEC 42001 can be grouped in the same way. Here is how it applies to AI risk:
- Plan: Identify potential AI risks and decide how to treat them (clause 6).
- Do: Put the risk treatments in place (clause 8).
- Check: Monitor and evaluate whether the treatments work (clause 9).
- Act: Make adjustments to improve risk management (clause 10).
Repeating the cycle helps organisations stay ahead of new AI risks as systems and their uses change.
What tools and strategies help with AI risk assessment?
For effective AI risk assessment, we recommend:
- A defined assessment method: Use risk assessment tools and criteria suited to AI, so results are consistent and can be compared over time.
- Ethical guidelines: Build ethical guidelines into the risk assessment so AI systems stay aligned with the organisation’s ethical commitments.
- Risk sources from Annex C: Check known AI risk sources, such as lack of transparency and explainability or the level of automation.
How do you identify and use AI opportunities ethically?
Clause 6.1 covers opportunities as well as risks. To use AI opportunities ethically, organisations should:
- Review AI systems regularly: Use internal reviews to find improvements or new uses that fit the organisation’s ethical commitments.
- Engage stakeholders: Talk to stakeholders to understand their needs and how AI can meet them responsibly.
What role does transparency play in managing AI risk?
Transparency helps manage AI risks and opportunities. It involves:
- Open communication: Explain how AI systems make decisions and what measures are in place to manage risk.
- Stakeholder involvement: Involve stakeholders in discussions about AI risks and opportunities to build trust and address ethical concerns.

Everything you need for ISO 42001
Structured content, mapped risks and built-in workflows to help you govern AI responsibly and with confidence.
How does an AIMS make AI systems traceable, transparent and reliable?
An AIMS makes AI systems traceable, transparent and reliable through the Annex A controls an organisation selects, recorded in its statement of applicability. The controls cover the AI system life cycle, the data AI systems depend on and the information given to people affected by them.
How can AI systems be audited?
Auditability supports trust and accountability in AI systems. Key measures include:
- Event logs: Deciding at which life cycle stages AI systems keep event logs, at minimum while the system is in use (control A.6.2.8).
- Internal audits: Auditing the AIMS at planned intervals to check it meets the organisation’s own requirements and those of ISO/IEC 42001 (clause 9.2).
How does an AIMS support data governance and explainability?
- Data governance: Defining and documenting data quality requirements (A.7.4), data provenance (A.7.5) and data preparation (A.7.6).
- Explainability: Using techniques that make AI decision-making understandable to humans. Annex C treats transparency and explainability as a potential AI objective.
How does an AIMS address robustness and safety?
Control A.6.2.4 asks the organisation to define and document verification and validation measures for each AI system, and the criteria for using them. Robustness and safety are both listed in Annex C as potential AI objectives. Organisations may choose methods such as:
- Stress testing: Checking how AI systems perform under extreme or unexpected conditions.
- Safety protocols: Setting rules AI systems must follow to reduce risks to users and data.
How can you improve AI system traceability?
To improve the traceability of AI systems, organisations can:
- Document the life cycle: Record design choices, data sources, verification results and changes for each AI system.
- Involve stakeholders: Bring stakeholders into development and review so decisions stay transparent and accountable.
What do the Annex A controls cover?
Annex A of ISO/IEC 42001 is a normative list of reference control objectives and controls. The table summarises each area. For control-by-control detail, see ISO 42001 Annex A controls explained.
| Annex A area | What it covers |
|---|---|
| A.2 Policies related to AI | Management direction for AI, set out in a documented AI policy |
| A.3 Internal organisation | AI roles and responsibilities, and a process for reporting concerns |
| A.4 Resources for AI systems | Documenting the data, tooling, system and computing, and human resources AI systems need |
| A.5 Assessing impacts of AI systems | Assessing impacts on individuals, groups and societies across the life cycle |
| A.6 AI system life cycle | Objectives for responsible development, design, verification and validation, deployment, operation, monitoring and event logs |
| A.7 Data for AI systems | Data quality, data provenance and data preparation |
| A.8 Information for interested parties | System documentation for users, external reporting of adverse impacts and communication of incidents |
| A.9 Use of AI systems | Processes and objectives for responsible use, and keeping to the intended use |
| A.10 Third-party and customer relationships | Allocating responsibilities between the organisation, suppliers and customers |
Who needs an AI management system?
Any organisation that develops, provides or uses AI systems can benefit from an AIMS, because ISO/IEC 42001 is written to apply regardless of size, type or nature. Annex D gives health, defence, transport, finance, employment and energy as examples of sectors where it can be used.
How does an AIMS work across different sectors?
For sector examples and how the standard fits with other management system standards, see ISO 42001 Annex D explained. A shared standard supports:
- Consistency in AI ethics: Applying the same ethical principles across AI development and deployment.
- Interoperability: Making it easier for organisations in different sectors to work together on AI.
- Benchmarking: Letting organisations measure their AI practices against an internationally recognised standard.
What are the benefits for the public sector?
In the public sector, an AIMS can help with:
- Public trust: Building public confidence in AI used in government services.
- Service delivery: Helping AI-driven public services stay fair, transparent and accountable.
- Legal and ethical obligations: Giving a structured way to manage the obligations that apply to public sector AI use.
What does an AIMS mean for AI-based products and services?
For organisations developing AI-based products and services, an AIMS can support:
- Quality assurance: Showing a commitment to high ethical and operational standards.
- Market differentiation: Standing out by following a recognised international standard.
- Customer trust: Building stronger relationships with customers through transparent and responsible AI use.
What are the legal and regulatory implications?
ISO/IEC 42001 is an international standard, not a law, so conforming to it does not on its own show that an organisation meets any AI law. It can still help with:
- Tracking legislation: Keeping AI practices in line with current and future AI-specific rules that apply to you.
- Reducing risk: Lowering the risk of legal challenges related to AI ethics, privacy and data protection.
- Working across borders: Giving one consistent approach for organisations operating in several countries.

Manage all your compliance, all in one place
ISMS.online supports over 100 standards and regulations, giving you a single platform for all your compliance needs.
How is an AIMS different from an ISMS or a QMS?
An AIMS governs the responsible development, provision and use of AI systems. An information security management system (ISMS) protects the confidentiality, integrity and availability of information. A quality management system (QMS) focuses on consistently providing products and services that meet customer and regulatory requirements.
| System | Standard | Main focus |
|---|---|---|
| AIMS (AI management system) | ISO/IEC 42001:2023 | Responsible development, provision and use of AI systems, including AI risk and impacts on people and society |
| ISMS (information security management system) | ISO/IEC 27001:2022 | Confidentiality, integrity and availability of information |
| QMS (quality management system) | ISO 9001:2015 | Products and services that consistently meet customer and regulatory requirements |
Can you run an AIMS alongside an ISMS?
Yes. ISO/IEC 42001 and ISO/IEC 27001:2022 both follow the harmonised structure for management system standards, so clauses 4 to 10 share the same numbering and titles. Annex D of ISO/IEC 42001 notes that security, privacy and quality topics are covered by ISO/IEC 27001, ISO/IEC 27701 and ISO 9001, and that objectives such as security and privacy are best managed together rather than separately for AI.
How does ISO/IEC 42001 relate to other AI standards?
ISO/IEC 42001 points to other AI standards for detail. It uses the terms defined in ISO/IEC 22989, refers to ISO/IEC 23894 for guidance on AI risk management, and refers to ISO/IEC 23053 for machine learning systems. Because these are international standards, they give organisations in different countries a shared reference for AI governance.
What are the challenges in building an AIMS?
Organisations may face challenges in aligning their AI practices with ISO/IEC 42001, including resource allocation for the work, keeping track of AI rules in different countries and keeping stakeholders engaged over time. Planning for these early, and reusing what already exists in an ISMS or QMS, makes them easier to manage.
What AI policies and objectives does an AIMS need?
Effective AI life cycle management under an AIMS starts with clear AI policies and objectives. Clause 5.2 asks top management to set an AI policy, and clause 6.2 asks for AI objectives that are measurable where practicable, monitored and updated. For a step-by-step route, see our ISO 42001 implementation step-by-step guide.
Which policies matter most for AI life cycle management?
To manage the AI life cycle well, your organisation should have policies that address:
- Data privacy and security: Rules for handling and protecting data throughout the AI life cycle.
- Ethical AI use: Ethical guidelines for AI development and deployment.
- Continual improvement: Regular review and improvement of AI systems.
How do you set measurable objectives for AI performance?
Measurable objectives let you track the performance and impact of AI systems. Objectives may include:
- Accuracy targets: Benchmarks for the accuracy of AI predictions or decisions.
- Efficiency improvements: The expected gains in operational efficiency.
- Ethical metrics: Measures of how well AI systems follow the organisation’s ethical guidelines.
How can you reduce bias and involve stakeholders?
Reducing bias and involving stakeholders are both part of ethical AI use. Strategies include:
- Diverse data sets: Training AI systems on diverse data and checking data for known or potential bias.
- Stakeholder consultations: Talking to stakeholders to understand their concerns and expectations of AI systems.
What does an AI system impact assessment cover?
ISO/IEC 42001 defines an AI system impact assessment as a formal, documented process for assessing how an AI system can affect individuals, groups of individuals and societies (clause 6.1.4 and control area A.5). It focuses on:
- Potential consequences: How the AI system’s deployment, intended use and foreseeable misuse could affect people.
- Ethical impact: The ethical implications of the AI system’s decisions and actions.
Why choose ISMS.online for your AI management system?
ISMS.online helps you build an AIMS and work towards ISO/IEC 42001 certification. With it you can:
- Create, store and find the policies and records your AIMS needs in one place.
- Run ISO/IEC 42001 alongside other standards, such as ISO/IEC 27001, and your other management systems in one platform.
- Organise your evidence so it is easy to find when you prepare for an audit.
- Get personalised advice from our team of experts as you work through ISO/IEC 42001 and its requirements.
- Use resources, including best practices, guidelines and case studies, to help your team understand the standard.
- Get answers to your questions, and guidance through setup, from our support team.
To see how ISMS.online can support your AIMS work, book a demo.
FAQs
Who issues ISO/IEC 42001 certificates?
Certificates are issued by accredited certification bodies after a certification audit. ISMS.online is a compliance platform, not a certification body: it helps you achieve certification by organising your AIMS and its evidence. Separately from any certification audit, the standard itself asks for internal audits (clause 9.2) and management reviews (clause 9.3) at planned intervals.
Do you have to apply every Annex A control?
No. Clause 6.1.3 asks the organisation to compare its chosen risk treatments with Annex A and produce a statement of applicability that justifies including or excluding each control. A control can be left out where the risk assessment shows it is not needed, and organisations can add controls of their own that Annex A does not list.
Does ISO/IEC 42001 cover the environmental impact of AI?
Yes, in two places. Clause 4.1 asks the organisation to decide whether climate change is a relevant issue, and Annex C lists environmental impact as a potential AI objective, noting that AI can have both positive and negative effects on the environment. How far to go, for example on energy use, is for the organisation to decide.
Does an AIMS cover AI from suppliers?
Yes. Control area A.10 covers third-party and customer relationships. It asks the organisation to allocate responsibilities between itself, its suppliers and its customers, and to make sure the services and products it gets from suppliers fit its approach to responsible AI (A.10.3).