


ISO 27001:2022 clause 9.1 requires an organisation to decide what to monitor and measure in its information security management system (ISMS), which methods to use, when and by whom, and when and by whom results are analysed and evaluated. It must keep documented evidence of the results and evaluate ISMS performance and effectiveness.
What does ISO 27001 clause 9.1 require?
Clause 9.1 sits in clause 9, Performance evaluation, alongside internal audit (9.2) and management review (9.3). It asks you to make and record six decisions about measuring your ISMS:
- What to monitor and measure: this explicitly includes your information security processes and your controls.
- Which methods to use: how you will monitor, measure, analyse and evaluate, so that the results are valid. The clause adds that the chosen methods should give results that are comparable and reproducible.
- When monitoring and measuring happen: the schedule or trigger for each measure.
- Who monitors and measures: a named role or person for each measure.
- When results are analysed and evaluated: for example monthly, quarterly or ahead of each management review.
- Who analyses and evaluates the results: which may be a different person from the one who collects the data.
Two further requirements complete the clause. Documented information must be available as evidence of the results, and the organisation must evaluate both its information security performance and the effectiveness of the ISMS as a whole.
Measurement only helps when someone looks at the results and decides what to do next.
Does ISO 27001 prescribe specific metrics?
No. Clause 9.1 tells you which decisions to make, not which numbers to report. You choose measures that fit your risks, your controls and your information security objectives. Counting activity alone, such as the number of incidents logged, can hide weaknesses in the system behind it, while very technical measures can be hard for management to act on. A short set of measures, each linked to a risk, control or objective, is usually more useful than a long list.
What does good clause 9.1 practice look like?
A working clause 9.1 set-up shows which controls are effective, which processes are falling behind and what is being done about it. Each measure has a purpose, a method, an owner and a schedule, and its results reach the people who can act on them.
A simple test for any measure: 'Does this tell us whether our information security risks are moving in the right direction?'
Book a demoHow do you decide what to monitor and measure?
Start from what the ISMS is meant to achieve. Your risk assessment, risk treatment plan and information security objectives (clause 6.2 asks for objectives that are measurable where practicable and monitored) already point to the processes and controls that matter most.
In practice, a clause 9.1 plan covers four things:
- Choosing what to watch: not every log or checklist tells you something useful. Pick the controls, processes and events that show whether the ISMS is working or whether risk is building up.
- Setting frequency and ownership: decide whether each measure is checked continuously, monthly or quarterly, based on how fast the related risk can change, and name who is responsible.
- Analysing, not just recording: numbers mean little until someone looks at trends and asks why. Combine figures with qualitative input such as incident reviews, staff interviews or changes in management’s risk appetite.
- Using results day to day: measures and dashboards are most useful when they surface a problem before an incident or audit does.
When the measurement schedule follows changes in risk and business priorities, reporting moves from describing what has already happened to warning about what could happen next.
Why do measures that are cut off from business risk fail?
Measuring for its own sake loses attention quickly. Measures that do not connect to a business priority tend to be ignored, and the weaknesses they could have shown later appear as audit findings or incidents.
Should you use standard metrics or build your own?
ISO 27001 sets the minimum, not the full picture. Common measures such as incident response time are a sensible starting point, but the set you keep should reflect your context, trace back to your risk appetite and be refined as threats and the business change.
How does clause 9.1 support decisions beyond compliance?
Treated only as a requirement to tick off, clause 9.1 produces reports that nobody reads. Used well, the same results help management decide where to spend time and money on security.
When clause 9.1 is applied properly, your measures can:
- Show material risks early: before they turn into incidents.
- Support investment decisions: with evidence for funding, staffing and resource requests based on risk.
- Explain the value of security work: to executives in terms they can act on.
- Trigger improvement: not only when something breaks, but when early indicators start to drift.
The same clause can produce a living dashboard or a file nobody opens. The difference is how the results are used.
How do you get leadership to use the results?
Present results as answers to questions management already has: are our main risks shrinking, are our controls working, and where do we need to act? When results are tied to those questions, the ISMS becomes part of business planning rather than a separate compliance exercise.
ISO 27001 made easy
An 81% Headstart from day one
We’ve done the hard work for you, giving you an 81% Headstart from the moment you log on. All you have to do is fill in the blanks.
Which ISMS metrics should you track?
The table below is a worked example of an ISMS metric set. Each row records the decisions clause 9.1 asks for: what is measured, how, by whom, how often, and what result prompts action. Adapt the measures, owners and thresholds to your own risks and objectives.
| Metric | How it is calculated | Owner | Frequency | Threshold for action | Linked risk or control |
|---|---|---|---|---|---|
| Incident response time | Time from detection to containment, by severity level | Incident manager | Monthly | Any incident over the agreed target time for its severity | Annex A 5.26 Response to information security incidents |
| Control review completion | Control reviews completed on time divided by control reviews scheduled | ISMS manager | Quarterly | Any review overdue past the agreed grace period | Risk treatment plan; clause 9.1 (controls) |
| Phishing simulation reporting rate | Staff who report the test email divided by staff who received it | Security awareness lead | Each campaign | Rate falls compared with the previous campaign | Annex A 6.3 Information security awareness, education and training |
| Critical vulnerability fix time | Critical vulnerabilities fixed within the agreed window divided by all critical vulnerabilities found | IT operations lead | Monthly | Any critical vulnerability open past the agreed window | Annex A 8.8 Management of technical vulnerabilities |
| Access review completion | Systems with a completed access review divided by systems in scope | System owners | Quarterly | Any in-scope system without a completed review | Annex A 5.18 Access rights |
| Progress on security objectives | Objectives on track divided by objectives set, using each objective’s own measure | ISMS manager | Before each management review | Any objective off track | Clause 6.2 Information security objectives |
Useful measures connect to business objectives such as reducing loss, keeping customer trust and maintaining continuity.
If a result would not change what you do, question whether the measure is worth keeping.
How do you combine numbers with qualitative evidence?
Figures show what is happening; people explain why. If incident numbers rise, pair the trend with incident reviews and feedback from the teams involved so that you fix the underlying cause rather than the symptom.
How often should you revisit your metric set?
Measures stay useful only if they still answer the question “what does management need to know now?” Review the set when risks, systems or objectives change, and retire measures that no longer lead to decisions. Whether you track access failures, phishing resilience or supplier alerts, each measure should earn its place.
What is the difference between analysis and evaluation in clause 9.1?
Clause 9.1 names analysis and evaluation as separate steps. In practice, analysis means working out what the results show, such as trends, outliers and likely causes. Evaluation means judging those results against your objectives and criteria to decide whether performance and effectiveness are good enough, and what to do if they are not.
Typical analysis and evaluation activities include:
- Spotting trends: a steady rise in denied access attempts may point to a change in attack techniques.
- Investigating outliers: a sudden, unexplained spike is worth a root-cause review rather than being dismissed as a one-off.
- Closing the loop: each significant finding should lead to a decision, whether that is a corrective action, a change to a control or a recorded decision to accept the result.
Results only change things when they lead to a decision someone owns.
What are the signs that results are not being used?
Reports that nobody reads, trends that are never discussed and findings without an owner all suggest that measurement has become a routine rather than a tool. A mature clause 9.1 process shows that reported trends are seen, discussed and, where needed, acted on.
How do you link clause 9.1 metrics to business risk?
Each measure should help manage a risk the business cares about, whether legal, reputational or financial. If a measure cannot be linked to one, question whether it belongs in the set.
| Risk area | Example metric | What it informs |
|---|---|---|
| Legal and regulatory | Time to report incidents internally and externally | Whether reporting deadlines in the laws and contracts that apply to you can be met |
| Reputational | Time to respond to security issues reported by customers or researchers | Customer trust and retention |
| Financial | Estimated impact of likely breach scenarios | Security budget and resilience planning |
How do you cut measures that do not earn their place?
Measures that nobody can justify tend to slip: schedules are missed, reviews stall and records go missing. Keep the indicators that map to real risks and external obligations, and drop those that cannot support a discussion about root causes with management.
In a management review, clear evidence carries more weight than opinion.
How do you set up a clause 9.1 process step by step?
A reliable clause 9.1 process builds measurement into management review and corrective action, applies it consistently and keeps the evidence. For more practical detail, see our guide on how to implement clause 9.1.
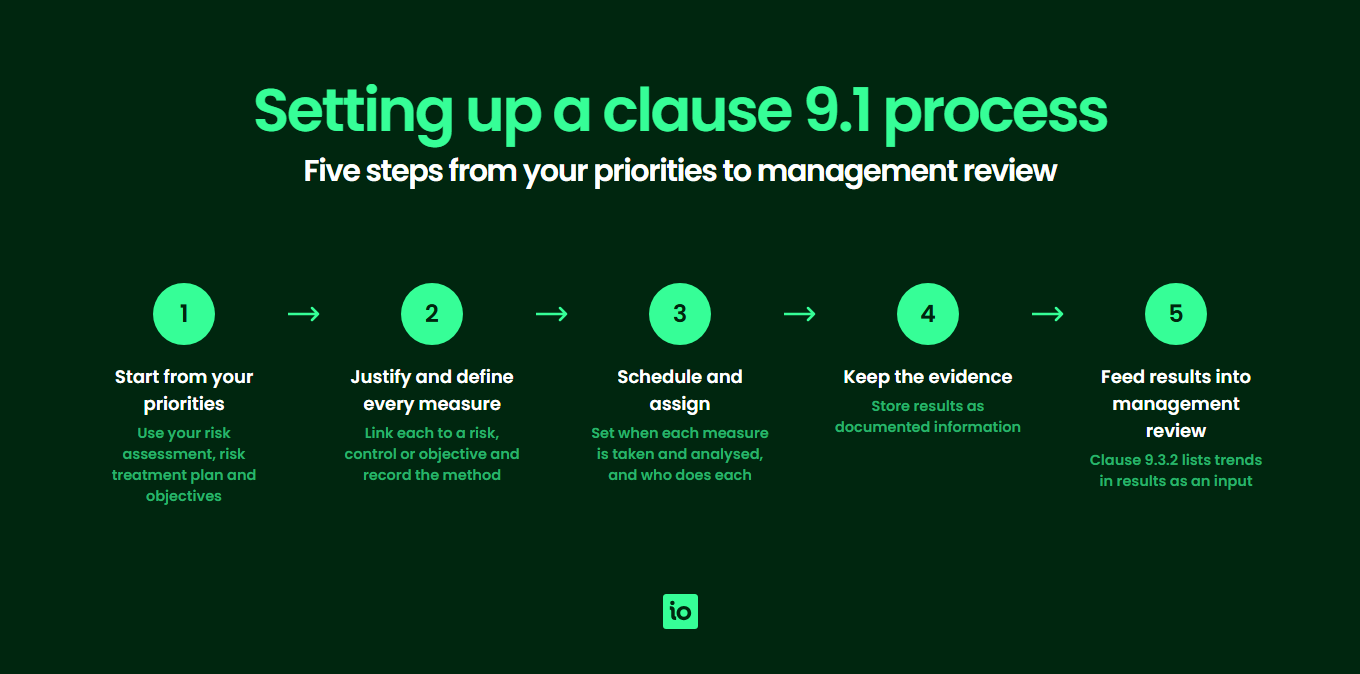
Five steps to put clause 9.1 in place
- Start from your priorities: use your risk assessment, risk treatment plan and objectives to decide which risks, assets and controls to measure.
- Justify and define every measure: link each one to a risk, control or objective, and record the method so that results are comparable and reproducible.
- Schedule and assign: set when each measure is taken and when results are analysed, and name who does each. In ISMS.online you can set review frequencies, send reminders and track completion.
- Keep the evidence: store results as documented information and link findings to the decisions and corrective actions they lead to.
- Feed results into management review: clause 9.3.2 lists trends in monitoring and measurement results among the inputs top management must consider, and nonconformities found through measurement are handled under clause 10.2.
Each cycle should leave risk smaller, not just better reported.

Manage all your compliance, all in one place
ISMS.online supports over 100 standards and regulations, giving you a single platform for all your compliance needs.
Where do clause 9.1 processes commonly go wrong?
Gaps in clause 9.1 rarely appear overnight. They build up through measures with no clear purpose, schedules that slip and data that is not connected to decisions. Common weaknesses include:
- No clear reason for a measure: an auditor or a customer doing due diligence may ask why a measure exists. Linking each one to a risk, control or process answers that question.
- Missed reviews: without reminders and owners, scheduled analysis is easy to skip, leaving gaps in the record.
- Lost evidence: results kept in personal files or spreadsheets can disappear when people change roles or leave. Version history and a central record keep the evidence intact.
Readiness is built through routine, not in the week before an audit.
How do you make measurement a standing part of management review?
Make clause 9.1 results a standing item on the management review agenda, record the findings, agree actions with owners and check progress at the next review. Our guide on how to implement clause 9 performance evaluation covers how monitoring, internal audit and management review work together.
How does clause 9.1 connect to the rest of ISO 27001?
Clause 9.1 provides much of the evidence the rest of the ISMS relies on. It draws on the risks and objectives set under clause 6, measures the processes and controls run under clause 8, and feeds management review (9.3) and improvement (clause 10).
| Clause | Main question | Who is involved | Typical output |
|---|---|---|---|
| 9.1 Monitoring, measurement, analysis and evaluation | Is the ISMS performing as intended, and are its processes and controls effective? | The people you name to measure, analyse and evaluate | Measurement results and evaluations kept as documented information |
| 9.2 Internal audit | Does the ISMS conform to your own requirements and to ISO 27001, and is it effectively implemented and maintained? | Internal auditors, run to a planned audit programme | Audit results reported to relevant management |
| 9.3 Management review | Is the ISMS still suitable, adequate and effective? | Top management, at planned intervals | Decisions on improvement opportunities and any changes needed |
The same clause number and title appear in other management system standards. If you also run a quality management system, see our page on ISO 9001 clause 9.1 to align the two.
Measurement links what you planned in clause 6 to what you improve in clause 10.
What should you do next?
If you are setting up or reviewing clause 9.1, start with a short checklist:
- List what you measure today and link each measure to a risk, control or objective.
- For each one, record the method, the schedule and who measures, analyses and evaluates it.
- Check that results are kept as documented information and reach management review.
A measure is only finished when someone has acted on its result.
Done this way, clause 9.1 gives management a regular, evidence-based view of whether the ISMS is working.
Why choose ISMS.online for clause 9.1?
ISMS.online is a compliance platform that helps you run clause 9.1 as part of your wider ISMS, keep the evidence in one place and achieve certification (certificates themselves come from accredited certification bodies). It helps you:
- Link measures to your ISMS: tie each measure to the risk, control or process it supports.
- Schedule reviews and reminders: set how often each measure is reviewed and who reviews it, and track completion.
- Use dashboards: show progress and results to the team and to management.
- Build action plans with owners: turn findings into tracked corrective actions.
- Keep audit trails and version history: keep a record of results and decisions when people change roles.
To see how ISMS.online can help you monitor, measure and evaluate your ISMS, book a demo.
Frequently Asked Questions
Does clause 9.1 require a written measurement procedure?
Clause 9.1 itself asks for documented information as evidence of the results, not for a written procedure. Clause 7.5.1 b) separately requires the documented information you decide is needed for the ISMS to be effective, so many organisations record their clause 9.1 decisions (what, how, when and who) in a short measurement plan. The format is your choice.
What changed in clause 9.1 between ISO 27001:2013 and ISO 27001:2022?
The six decisions are the same in both editions. In the 2022 edition, the point that methods should produce comparable and reproducible results moved from a note into the requirement on methods; the evidence wording changed from retaining documented information to having it available; and the requirement to evaluate performance and effectiveness moved from the start of the clause to the end.
How many metrics should a small organisation track?
ISO 27001 sets no number. A small organisation can meet clause 9.1 with a handful of measures, as long as they cover its key processes and controls, follow the six decisions and produce kept evidence. It is easier to add a measure later than to maintain one nobody uses.
Can the same person collect and evaluate the results?
Clause 9.1 asks you to decide who monitors and measures and, separately, who analyses and evaluates; it does not say they must be different people. Many organisations still split the roles so that the person judging the results is not the one producing them, which gives management a more balanced view.
Can monitoring for clause 9.1 be automated?
Yes. The clause leaves the choice of methods to you, provided they give valid results. Automated data collection from systems and tools can make results more consistent, but someone still needs to analyse and evaluate them and record what was decided.
What evidence might an auditor or customer ask to see for clause 9.1?
An auditor or a customer doing due diligence may ask to see the list of what you measure with its methods, schedules and owners; records of the results; evidence that results were analysed and evaluated; and how they reached management review and led to actions.
Useful records to keep together
- Your measurement plan covering the six clause 9.1 decisions.
- Dated results and the analysis of trends.
- Management review minutes and the actions that followed.