





ISO 27001:2022 clause 8.2 requires an organisation to carry out its information security risk assessments at planned intervals it sets itself, and also whenever significant changes are proposed or take place, using the risk criteria defined under clause 6.1.2. The organisation must keep documented information of the results of every assessment.
Why Does ISO 27001:2022 Clause 8.2 Risk Assessment Matter More Than Ever?
Modern organisations are defined not by the risks they face, but by how confidently they anticipate and manage them. Clause 8.2 in ISO 27001:2022 is where your risk method turns into real, recorded results, and those results shape the security decisions that protect your resilience, performance and the trust others place in you.
Risk assessment isn’t just a check—it’s a scoreboard for the credibility of your entire operation.
Clause 8.2 asks you to put your risk assessment process into practice: identify, analyse and evaluate the risks that could disrupt, delay or degrade your business. These aren’t theoretical compliance exercises. A living risk assessment process is a reputational asset, a negotiating chip in audit and the backbone of crisis avoidance. If your board can’t explain your process—or your leadership can’t show stakeholders active ownership—security gaps become tomorrow’s headlines.
Cyberattacks, new legal obligations and shifting customer trust pile more weight onto every missed risk. Relying on static registers or IT-only inventories is no longer enough. A business-wide, methodical and clearly defensible risk process drives strategy and resource allocation, and enables CISOs and compliance leads to say, “We know what matters most, and we can prove it.”
Organisations that invest in real-time risk insight come out ahead—faster deals, fewer losses, and stronger partnerships.
What Exactly Does Clause 8.2 Require of Your Risk Assessment Process?
Clause 8.2 requires you to perform information security risk assessments at planned intervals and when significant changes are proposed or occur, applying the criteria you set under clause 6.1.2, and to retain documented information of the results. The intervals are yours to define; the standard does not fix a frequency.
How Does Clause 8.2 Differ From Clause 6.1.2 and Clause 8.3?
- Clause 6.1.2 (planning): you define and apply the risk assessment process, including risk acceptance criteria, criteria for performing assessments and how you identify, analyse and evaluate risks. You keep documented information about the process.
- Clause 8.2 (operation): you run that process on a schedule and when significant change happens, and keep the results.
- Clause 8.3 (operation): you implement the risk treatment plan and keep the results of the treatment.
Put simply, risk assessment finds, analyses and ranks your information security risks; risk treatment decides and carries out what you will do about them. ISO/IEC 27005:2022 gives guidance on managing information security risks in support of these ISO 27001 requirements. To set up the process itself, see our guide on how to implement Clause 6.1.2.
What Are the Core Steps?
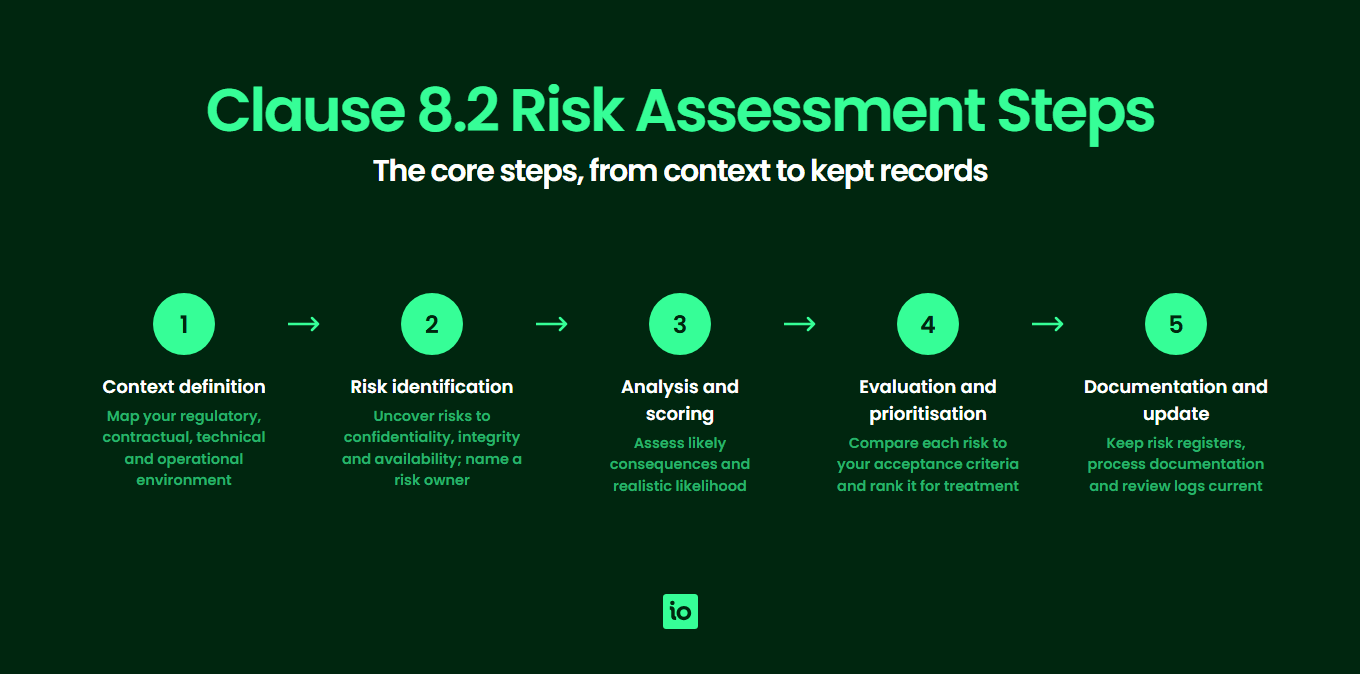
- Context Definition: Map your regulatory, contractual, technical and operational environment, building on your work on understanding the organisation and its context. Think beyond IT—include legal exposure, third-party risk and market reputation.
- Risk Identification: Bring together IT, Legal, HR and operational owners to uncover risks to the confidentiality, integrity and availability of information across systems, data, suppliers and people, and name a risk owner for each.
- Analysis and Scoring: Assess the likely consequences and the realistic likelihood of each risk, using tested qualitative or quantitative models that your board, your auditors and your risk owners can all understand.
- Evaluation and Prioritisation: Compare each risk to your acceptance criteria and rank it for treatment. Escalate business-critical pain points automatically—don’t let serious risks languish in a spreadsheet.
- Documentation and Update: Keep risk registers, process documentation and review logs current. Outdated files spark more suspicion than trust.
If your board can’t read your risk register and see your logic, you’re inviting unwelcome questions.
What Makes a Clause 8.2 Assessment Hold Up?
The strongest assessments are aligned with your business objectives rather than copied from a template. Clause 6.1.2 asks that repeated assessments produce consistent, valid and comparable results, so your method needs to fit your operations, sector and stakeholder interests and be applied the same way each time.
A good risk assessment under Clause 8.2 is:
- Systematic: Consistently executed and improved.
- Contextual: Mapped to the realities of your business, not abstract theory.
- Defensible: Traceable in decision and record, with clear ownership.
Which Pitfalls Still Undermine Most Risk Assessments?
Even mature programmes can falter. Here’s where organisations often stumble:
- Narrow Focus: IT-led processes miss legal, supply chain and reputational risks.
- Stale Data: Waiting for the next scheduled review lets emerging threats slip through; significant changes should trigger an assessment too.
- Template Thinking: Borrowed risk matrices miss what actually matters in your environment.
- Weak Prioritisation: Treating every risk as equal drains resources and misses what could cause a major incident.
- Minimal Leadership Involvement: ‘Delegated’ risk assessments end up unread and unacted-upon.
Templates never reveal the risk unique to your business model. They lull decision-makers into a false sense of security.
A live risk process should drive budget, guide control choices and shape incident response—otherwise it’s just paperwork, not protection.
ISO 27001 made easy
An 81% Headstart from day one
We’ve done the hard work for you, giving you an 81% Headstart from the moment you log on. All you have to do is fill in the blanks.
Who Needs to Be Involved to Make Clause 8.2 Work?
ISO 27001:2022 clause 6.1.2 asks you to identify a risk owner for each risk, so accountability is built into the process.
Critical Roles and Responsibilities
- Compliance and Regulatory Leaders: Anchor frameworks to both legal obligations and strategic business intent.
- IT and System Custodians: Own asset and vulnerability mapping, but don’t stop there.
- Operations and HR: Capture people-driven exposures—social engineering, insider threats and policy compliance.
- Legal Advisors: Provide horizon scanning for new liabilities and regulatory changes.
- Executive Sponsors and Board: Set appetite, challenge assumptions and own escalations.
Engaged leadership goes beyond oversight. Well-run organisations make sure directors regularly receive and review tangible risk evidence, so they’re never caught off guard or unable to back up their decisions.
Accountability means every major risk has a name beside it—and leadership ready to act.
What Evidence Shows Your Clause 8.2 Work Under Audit?
If it isn’t documented, it’s hard to show it was done. An auditor or customer doing due diligence may ask for records that are clear, current and tell a logical story from identification to decision.
Which Records Should You Keep?
ISO 27001:2022 names two pieces of documented information here: information about your risk assessment process (clause 6.1.2) and the results of your risk assessments (clause 8.2). The table adds supporting records many organisations keep. The review frequencies are examples of common practice, not requirements: the standard leaves the planned intervals for you to define.
| Record | What It Shows | Example Review Frequency |
|---|---|---|
| Risk Assessment Methodology | Steps, logic, business-fit | Annually or post-change |
| Risk Registers | Assets, threats, scoring, clear owners | Quarterly |
| Review / Board Minutes | Decisions, escalations, response actions | Semi-annually or annually |
| Incident Feedback Logs | How lessons learned put new risks on the radar | After every incident |
| Training and Awareness | Proof stakeholders know their roles | Annually, or after change |
These aren’t box-ticking exercises. Each document shows your own team, and anyone reviewing your ISMS, that risk is real, owned and acted upon in your organisation.
The quality of your evidence is the frontline between peace of mind and post-incident chaos.
How Do Ongoing Review and Improvement Become the Real Differentiator?
Clause 8.2 builds repetition into risk assessment through planned intervals and change-triggered assessments, and clause 10.1 asks you to continually improve the ISMS as a whole. The results of risk assessment and the status of the risk treatment plan are also inputs to your Clause 9.3 management review. The most resilient organisations see risk assessment as a muscle to be exercised, not a document to be filed.
Continuous Improvement Embedded in Security Practice
- Regular Risk Workshops: Pull leaders from across your business to challenge current priorities and surface new threats.
- Scenario and Stress Testing: “What if?” sessions that prove resilience isn’t theoretical.
- Benchmarking: Track your approach against sector peers and evolving regulatory alerts.
- Rapid Method Updates: Improve your models after every incident, not just at year-end.
- Transparent Reporting: Show your board, your team, and—where it counts—your partners that risk agility is a habit, not an aspiration.
Empowered teams view risk as a lever for great decisions—not a shadow to be feared.
What Should You Do Next With Clause 8.2?
Start by checking that your risk assessment methodology states your planned intervals and the kinds of significant change that trigger a new assessment, and that the results of each assessment are kept. Then follow our step-by-step guide on how to implement Clause 8.2. With ISMS.online, you can build and maintain a live risk framework that your organisation owns.
Why Choose ISMS.online for Clause 8.2 Risk Assessment?
ISMS.online gives your team living tools, not just archives, by automating the mechanics of risk assessment and monitoring. It helps you:
- Keep your risk records in one place, so every update, action and review is easy to trace.
- Show a clear trail from assessment to action, ready for leaders and anyone reviewing your ISMS.
- Run each assessment cycle with version control, live notifications and board-friendly reporting.
- Automate handoffs, escalation paths and follow-through between finding a risk and treating it.
- Log inputs from people across departments, highlight contributors and escalate unresolved risks.
- Respond to business changes quickly and document every move for leadership or external review.
The faster you surface a risk, the less you’ll need to explain to your board and your market.
To see how ISMS.online can help you run and record your clause 8.2 risk assessments, book a demo.

Manage all your compliance, all in one place
ISMS.online supports over 100 standards and regulations, giving you a single platform for all your compliance needs.
Frequently Asked Questions
What sets ISO 27001:2022 Clause 8.2 risk assessments apart from compliance checkbox routines?
A checkbox routine asks only whether an assessment was completed. A useful Clause 8.2 assessment shows how each risk ties to your objectives, reputation and real-world requirements, and an auditor or customer doing due diligence may ask you to show that link. That means moving past IT silos so risk identification and scoring connect with your current operations, market conditions and legal obligations. Each risk evaluation should be understandable even at the boardroom table—no “security-only” jargon or copy-pasted ratings from generic spreadsheets.
Your risk assessment should give the board confidence, not confusion.
Set evaluation criteria that capture input from every level, not just tech-savvy teams. Update and evolve those metrics whenever a threat changes or the business pivots, and build evidence into every rating. With ISMS.online, you’re not just showing completed paperwork; you’re demonstrating a responsive, defensible risk process that adapts as your world changes.
How does a living risk assessment process protect you beyond audit season?
- Criteria reflect actual business drivers, not generic templates or old frameworks.
- Change logs and incident feedback drive continuous updates, keeping your approach fresh.
- Every decision connects to value—compliance, yes, but also revenue, reputation and resilience.
- ISMS.online provides a clear trail from assessment to action, ready for leaders and anyone reviewing your ISMS.
How does a modern Clause 8.2 risk assessment actually unfold—step by step—without wasted cycles?
A static risk register looks impressive—until real threats emerge from unexpected corners. The modern Clause 8.2 process begins by mapping your environment: understand your industry, current regulations and key business processes. Pull in fresh perspectives from operations, HR, sales, finance and even third-party vendors—risks are everywhere, not just in IT closets. Document risks to assets, people, processes and supply chains. Score and prioritise threats with transparent reasoning, making it obvious why risks matter now and what takes precedence.
Limiting risk reviews to security teams means leaving half your exposures in the shadows.
What does an effective risk assessment workflow look like in action?
- Define business context: Pin down what matters—today’s most crucial operations and crown-jewel assets.
- Broad identification: Actively gather risks from across departments, not just IT dashboards.
- Transparent scoring: Use business-language metrics everyone can understand.
- Assign clear accountability: Every risk needs a named owner and a stated next action.
- Track and refine: Make every feedback loop, incident or change visible in real time.
ISMS.online automates this cycle, ensuring version control, live notifications, and board-friendly reporting at every step. You achieve more than compliance—you build a track record of proactive control.
Did ISO 27001:2022 change what Clause 8.2 requires?
No. The requirement in clause 8.2 of ISO/IEC 27001:2022 reads the same as clause 8.2 of the 2013 edition: assess information security risks at planned intervals and when significant changes are proposed or occur, using the criteria from clause 6.1.2 a), and keep the results. The standard does not require continuous or real-time assessment; you decide the intervals and which changes count as significant.
Treat your risk register as an asset portfolio—active, monitored, and worth investing in.
What many organisations do differently is how they apply the clause:
- Event-driven updates: Write down which changes trigger a fresh assessment, so you don’t wait for the next scheduled review.
- Tailored methodology: Fit your process to your sector, and revisit it as your market, legal obligations or structure change.
- Full transparency: Give every risk a clear line from identification to action, with reasoning visible to executives and to anyone reviewing your ISMS.
ISMS.online helps you respond to business changes swiftly and document every move for leadership or external review, so you are not racing to show your work after the fact.
How do you keep Clause 8.2 records linked so they stand up to audit and executive questions?
No risk programme survives on trust alone. The value of your records comes from how well they connect: a methodology that details how you classify, score and treat risk; a risk register that is version-controlled and always points to action status and ownership; and logs of leadership discussions, decisions and incident responses. Most important: show how feedback and lessons learned trigger actual updates to the register.
The documentation you share is proof of discipline—your daily actions become your audit defence.
ISMS.online is built to capture and surface all these records in one place, so every update, action and review is easy to trace, defend and improve.
How should you connect Clause 8.2 risk findings directly to Clause 8.3 risk treatment—and why does this move you from compliance to operational strength?
A risk register that just lists vulnerabilities is a liability itself. Under ISO 27001:2022, the risks you evaluate and prioritise are the input to your risk treatment process (clause 6.1.3), and clause 8.3 requires you to implement the resulting treatment plan and keep the results. In practice, that means each significant risk gets a defined response, a real owner and a clear timeline, and leaders and customers can see accountability and closure on every major exposure.
Risks ignored become weaknesses exploited—transparency is your shield.
To get it right:
- Cross-link every risk to a treatment action—mitigate, transfer, accept, avoid.
- Assign a real person for every plan, never a “ghost” owner.
- Maintain a timeline for review and evolution—no risk sits forgotten.
- Use ISMS.online to automate these handoffs, escalation paths and follow-through—your risk process won’t stall between discovery and action.
That’s how you close the loop: risk management stops being a theory and starts running as part of your actual business.
Why does broad participation across your organisation determine the success of Clause 8.2 risk assessments under ISO 27001:2022?
A high-functioning risk assessment under Clause 8.2 demands more than buy-in from IT or compliance—the conversations must span every major business function. Risks live in HR, procurement, legal, and especially in places leadership rarely visits. The more voices engaged in the risk programme, the more blind spots you close and the more resilient your business becomes.
Overlooked risks often hide at the edges—discovered too late because the right people weren’t heard.
How do you embed an “all-in, all-voices” risk culture?
- Assign responsibility for risk input across departments, not just the security team.
- Schedule leadership and cross-functional reviews often enough for real input, not just signatures.
- Use plain language to demystify risk scoring, making it accessible to every participant.
- Let ISMS.online’s user management log inputs, highlight contributors, and escalate unresolved risks.
- Publicly celebrate teams or individuals who flag risks that lead to real business savings or disaster prevention.
This is about more than compliance—creating this culture means your risk assessment not only survives audits, but actually improves business performance and reputation.