





An ISO 27001 asset inventory is a maintained record of the information your organisation holds and the other assets that support it, such as people, hardware, software, services and sites, each with a named owner and a classification. ISO 27001:2022 Annex A control 5.9 covers developing and maintaining this inventory, including its owners.
Why do you need an asset inventory?
You will normally need to create an inventory of your organisation’s information assets to:
- Build an effective Information Security Management System (ISMS)
- Achieve ISO 27001 compliance or certification
When we talk about information assets we find that most people think about things like laptops and servers. But there are many other items you’ll need to consider. People, intellectual property and even intangible assets like your organisation’s brand can all fit into your Asset Inventory.
Once you’ve developed your Asset Inventory your next step is to undertake three exercises:
- Filtering
- Prioritisation
- Categorisation
Then you’ll need to map the risk to your assets by using those categories you’ve just identified.
Developing your Asset Inventory can seem quite complicated at first. But if you’re using ISMS.online you don’t really need to know the ins and outs before you get started.
If this is your first ISO 27001 implementation, you’ll benefit greatly from our Virtual Coach feature. This series of videos is available 24/7 within the platform. It guides you through your certification journey, including developing your Asset Inventory.
What should be included in an ISO 27001 asset inventory?
In the current edition, ISO 27001:2022, the control on Annex A 5.9 inventory of information and assets covers information and the other assets associated with it, not just physical equipment. That means anything of value to the organisation where information is stored, processed or accessed. It is the information that is of real interest, less so the network or device itself, although those are still assets and need to be protected.
The inventory does not have to be a single list. The guidance in ISO 27002 control 5.9 says it can be a set of inventories kept by the teams responsible for them, for example separate lists for information, hardware, software, facilities and people. It also says the inventory should be accurate, up to date and consistent with any other inventories you keep, and should record where each asset is located where that is relevant.
The table below sets out the main asset categories, with examples and an example owner for each.
| Category | Examples | Typical owner (example) |
|---|---|---|
| Information (or data) | Customer records, HR files, contracts, financial records | Head of the team that creates or uses the information |
| Intangibles | Intellectual property, brand and reputation | Senior leader responsible for the product or brand |
| People | Employees, temporary staff, contractors, volunteers | Line manager or HR lead |
| Hardware | IT servers, network equipment, workstations, mobile devices | IT manager |
| Software | Purchased or bespoke software | IT manager or the business owner of the system |
| Services | The service provided to end-users, such as database systems or email | Service or supplier manager |
| Locations and buildings | Sites, buildings, offices | Facilities manager |
The owners shown are examples only. Choose the person or group in your organisation with the responsibility and authority for the asset.
How can you group assets?
Any type of asset can be grouped together logically according to a number of factors such as:
- Classification – e.g. public, internal, confidential etc
- Information type – e.g. personal, personal sensitive, commercial etc
- Financial or non-financial value
An auditor or a customer doing due diligence may ask to see an inventory, or inventories, that cover all the relevant assets within the scope of the ISMS. ISO 27002 control 5.9 guides that each asset should have an owner, which can be a person or a group, and a classification.
What does an ISO 27001 asset inventory example look like?
A simple inventory records, for each asset, what it is, its category, its owner, its classification, where it is held and the risks it is linked to. The example below is illustrative; your columns and classification levels should match your own policies.
| Asset | Type | Owner | Classification | Location | Linked risk |
|---|---|---|---|---|---|
| Customer database | Information | Head of Sales | Confidential | Cloud CRM service | Unauthorised access to customer personal data |
| Staff laptops | Hardware | IT Manager | Internal | Head office and home workers | Loss or theft of a device |
| Payroll software | Software | Finance Director | Confidential | Supplier-hosted service | Supplier outage delays payroll |
| Email service | Service | IT Manager | Internal | Cloud service | Phishing leads to account takeover |
| Product source code | Intangible | Head of Engineering | Confidential | Code repository | Code is leaked or changed without approval |
| Main office | Location | Facilities Manager | Internal | Head office | Unauthorised entry to the building |
For step-by-step help with putting the control in place, see our guide on how to implement Annex A 5.9.
Who should the asset owner be and what are their ISO 27001 responsibilities?
The owner is not necessarily the legal or physical holder of the asset but the person or group that has the responsibility and matching authority to ensure that, among other things:
- Assets are inventoried;
- Assets are correctly classified and protected, and the classification is reviewed from time to time;
- Access restrictions match the asset’s classification and are reviewed periodically; and
- Assets are handled securely when being deleted or destroyed, and are then removed from the inventory.
Day-to-day responsibilities for asset management (e.g. updating the inventories, carrying out audits etc) can be delegated but the ultimate responsibility for ensuring correct management remains with the relevant asset owner.
It is the asset owner who is responsible for setting the protection requirements for the asset, such as access restriction, in line with organisational policies and standards. ISO 27002 control 5.9 also suggests reassigning ownership when an owner leaves or changes role, so no asset is left without one.
If your organisation also falls under NIS 2, our guide to NIS 2 asset inventory with ISO 27001 mapping shows how the two sets of requirements line up.
How does an ISO 27001 asset inventory relate to GDPR?
Under the General Data Protection Regulation (GDPR), Article 30 requires controllers and processors to keep a record of their processing of personal information, with a limited exemption for some organisations employing fewer than 250 people. Article 32 requires security measures appropriate to the risk to personal data. An ISO 27001 asset inventory that already lists where personal information is held, together with the risk assessment linked to it, gives you a sound base for meeting GDPR requirements too.
Should you use a template or tool to manage your asset inventory?
There are many example templates for asset inventories/registers available and these follow a simple spreadsheet approach which are just as easy to build yourself.
However, a spreadsheet is a static document and whilst they are great for financial modelling and basic stuff, they are not so good for demonstrating how the asset links to the identified risks, the relevant policies and controls, or the other dynamic work of an information security management system.
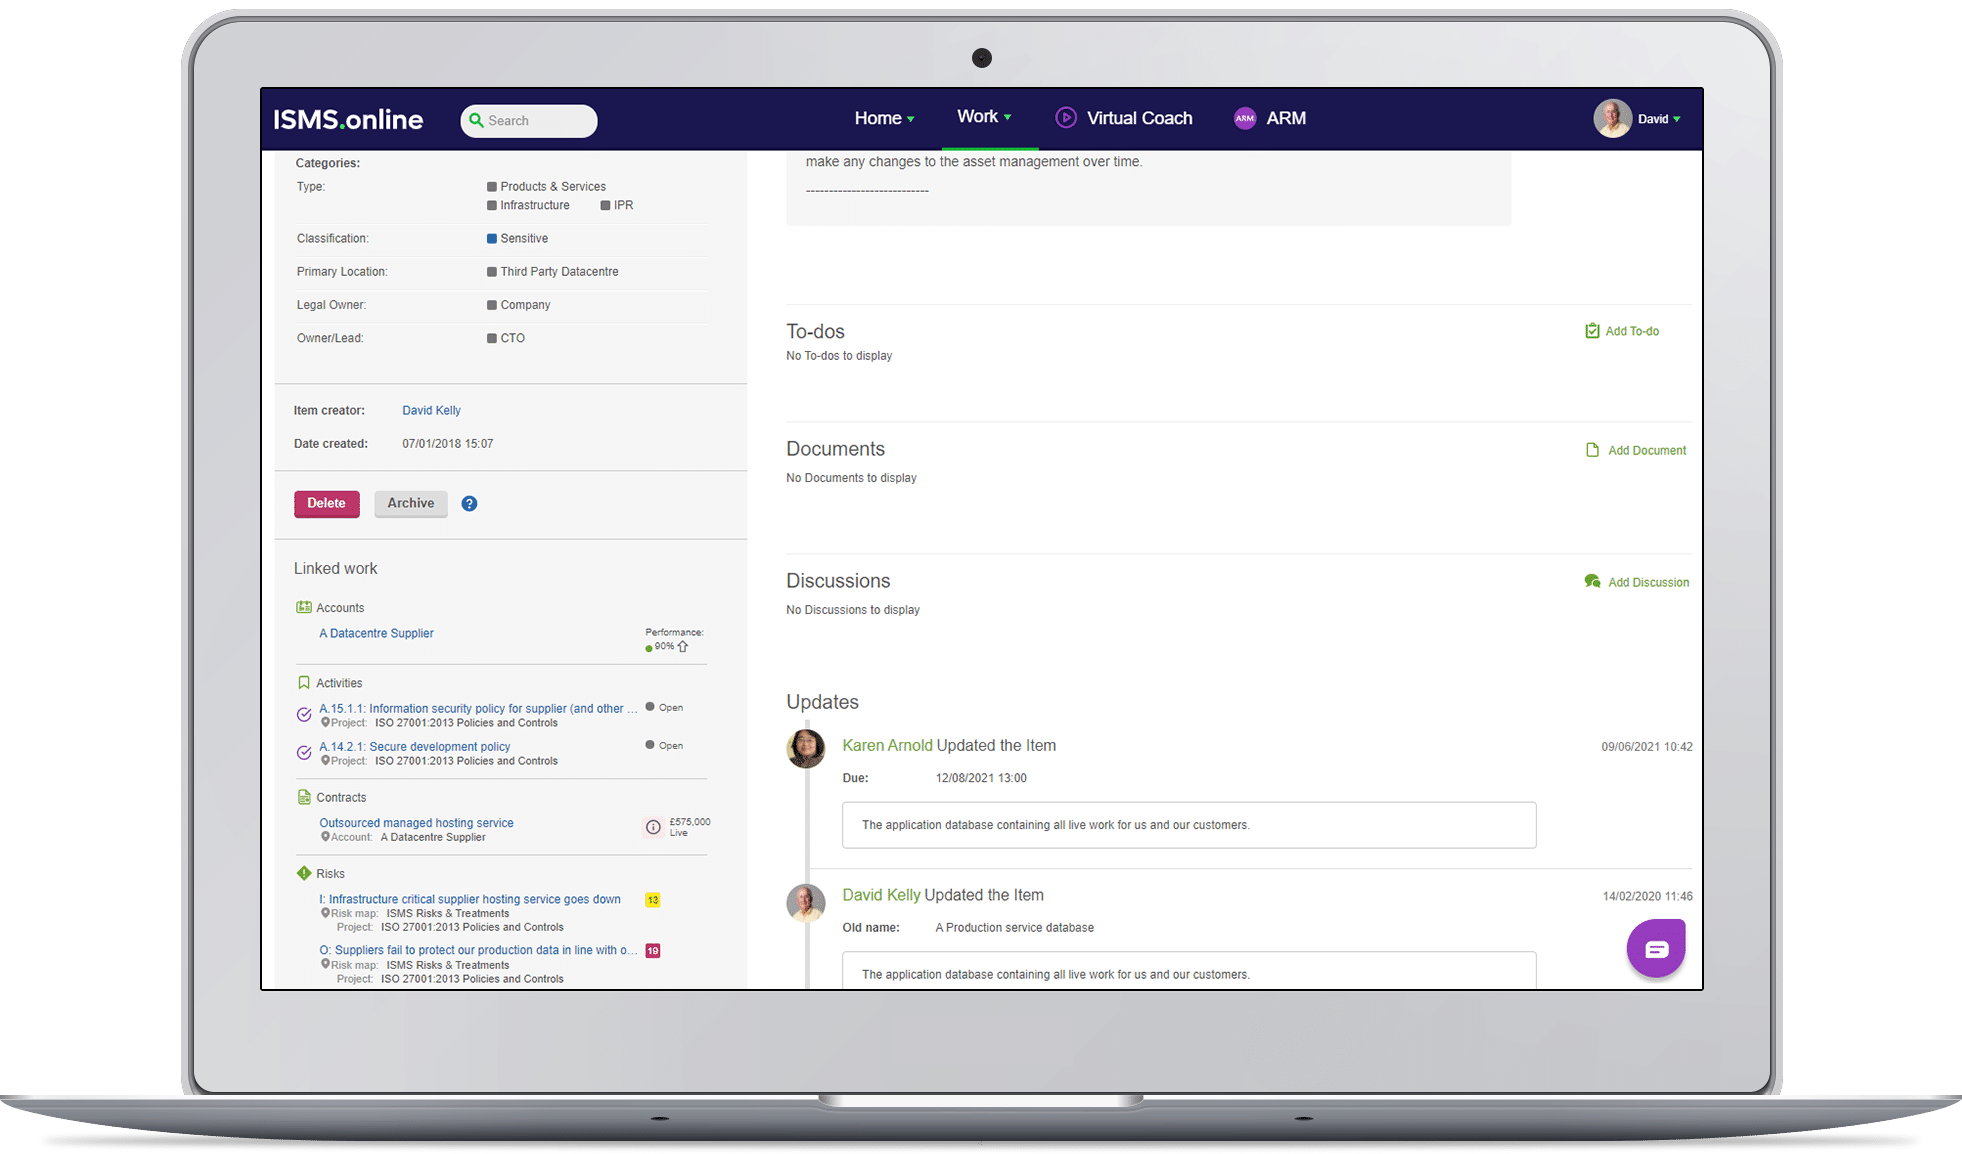
A good technology tool for asset inventories will come pre-configured, with the option to customise to suit your own classifications, allow you to assign owners, due dates and reminders and to capture all the evidence required in one secure location.

Also consider an information security management tool that allows you to assign values to your assets as this will help you prioritise risk assessments and understand any potential impact of security incidents, events or breaches.
Finally, the best tools will come with the ability to easily link the asset to risks on your risk treatment plan, to your ISMS controls, supply chain and any other actions in the ISMS that demonstrate your assets are well protected.
So, building your own asset spreadsheet may have no perceived cost but will have the challenge of much higher management and coordination with the other parts of the ISMS, especially if you are aiming for ISO 27001 certification. Or you can take a longer-term view and invest in a specialist asset management tool. But they’re often complex and detail heavy. Information asset management could well become a full-time job in its own right. And you’ll still need to link your tool with the rest of your ISMS.
Instead of reaching for a spreadsheet or a stand-alone specialist tool, we’d recommend looking for an ISMS platform that includes its own asset inventory tool and links it to your risks, controls and Statement of Applicability.
Why choose ISMS.online for your asset inventory?
ISMS.online includes its own asset inventory tool and links each asset to the rest of your ISMS work. It helps you:
- Start with an asset inventory that comes pre-configured, then customise it to suit your own classifications.
- Assign asset owners, due dates and reminders.
- Capture the evidence for internal and external audits in one secure location.
- Link each information asset to the risks it faces and on to the controls needed in the risk treatment.
- Move from a control to your Statement of Applicability and update it with the justification for implementing that control.
- Link assets to your supply chain and the other actions in your ISMS that show your assets are well protected.
To see how ISMS.online can help you build and maintain your ISO 27001 asset inventory, book a demo.
FAQs
Is an asset inventory mandatory for ISO 27001?
You will normally need one. In ISO 27001:2022 the inventory sits under Annex A control 5.9, and your Statement of Applicability records the justification for each control you implement.
How do you keep an asset inventory up to date?
Update it as assets change rather than treating it as a one-off list. In practice that means removing assets once they have been securely deleted or destroyed, reviewing classifications and access restrictions from time to time, and reassigning ownership when an owner leaves or changes role.