





An interested party is any person or organisation that can affect your information security decisions and activities, be affected by them, or believe it is affected. Clause 4.2 of ISO/IEC 27001:2022 asks you to work out which interested parties matter to your information security management system (ISMS), what they require, and which of those requirements the ISMS will address.
What does ISO 27001 clause 4.2 require?
Clause 4.2, “Understanding the needs and expectations of interested parties”, asks your organisation to determine three things:
- a) the interested parties that matter to your ISMS;
- b) the relevant requirements of each of those parties;
- c) which of those requirements your ISMS will address.
Point c) is new in the 2022 edition. The 2013 edition asked only for the relevant parties and their requirements relevant to information security, so the 2022 wording makes you record a decision about what the ISMS will and will not take on.
A note in the clause explains that these requirements can come from laws and regulations as well as from contractual obligations. In practice, many of the most important requirements come from laws that apply to you and from the contracts you sign with customers and suppliers.
The term “interested party” is often used in the same way as “stakeholder”. For a short definition you can share with colleagues, see our interested party glossary definition.
Who counts as an interested party in ISO 27001?
Any person or organisation whose needs or influence touch your information security can be an interested party. The list below groups common examples.
Internal interested parties
- Top management and the board, who set risk appetite and business priorities
- Employees and contractors, who handle information every day
- Functions such as HR, legal, IT, procurement, sales and operations, whose practices can create or reduce security risk
- Owners, shareholders and investors
- Subsidiaries and overseas branches, which may face different laws and customer demands
External interested parties
- Customers, including the specific security terms in their contracts
- Suppliers and service providers, such as cloud hosting, outsourced IT and software vendors
- Business partners and resellers
- Regulators, such as the UK data protection regulator (the Information Commission, which took over from the Information Commissioner on 30/09/2026) and, if the rules apply to you, the competent authority for your sector under the Network and Information Systems Regulations 2018
- Insurers, whose cyber policies may set security conditions
- Authorities and specialist groups you keep in contact with, such as law enforcement and security forums (see Annex A controls 5.5 and 5.6)
- Local communities and the public, where an incident could affect them
Guidance bodies such as the National Cyber Security Centre (NCSC) publish security advice rather than enforcing your obligations. Many organisations still watch their guidance as a source of new expectations.
Start with the obvious parties, then look for the ones that are easy to miss: overseas branches, niche suppliers brought in by project teams, and insurers.
How do you identify interested parties and their requirements?
A repeatable method makes the list easier to defend and to keep current. A common approach has six steps:
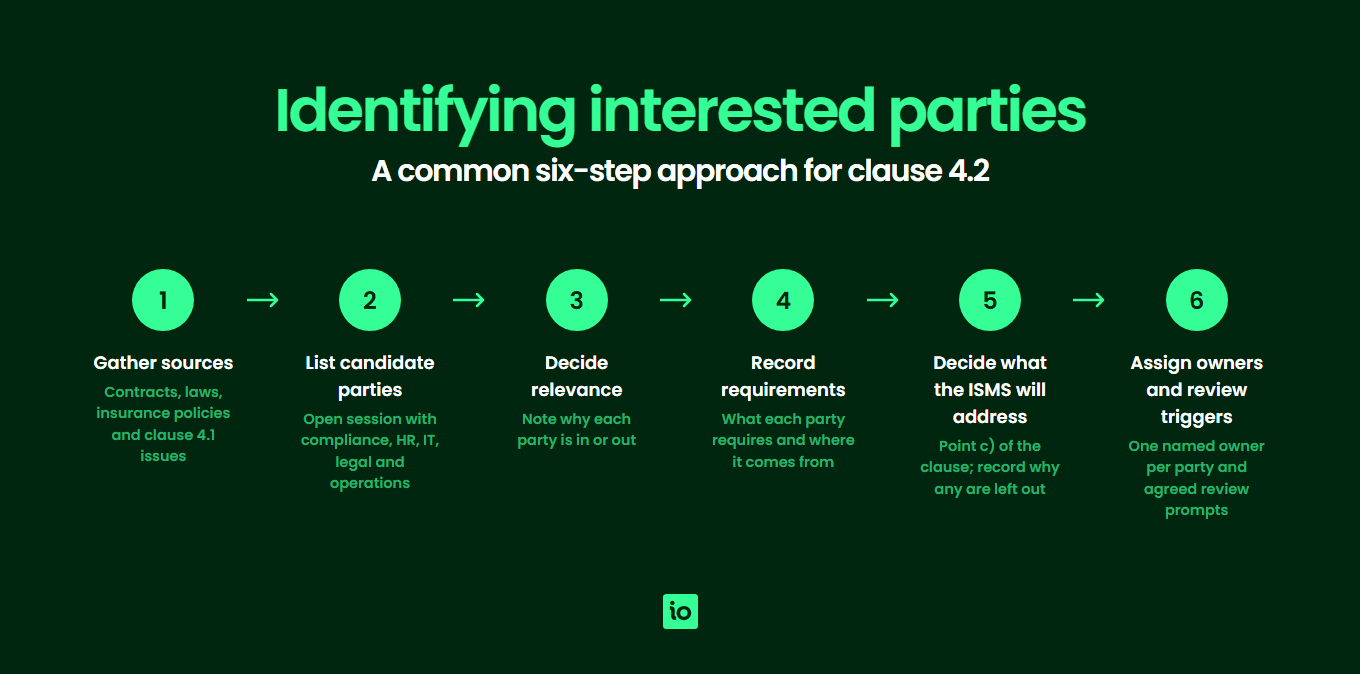
- Gather sources. Bring together the organisation chart, customer and supplier contracts, service level agreements, insurance policies, the laws and regulations that apply to you, and the internal and external issues you identified under clause 4.1.
- List candidate parties. Run an open “who touches our sensitive information, or relies on it?” session with people from compliance, HR, IT, legal, procurement and operations.
- Decide relevance. For each candidate, decide whether it matters to the ISMS and note why it is in or out.
- Record requirements. For each relevant party, write down what it requires and where that requirement comes from: a law, a contract term, a policy or an expectation.
- Decide what the ISMS will address. Mark which requirements the ISMS will cover, as point c) of the clause asks, and record why any are left out.
- Assign owners and review triggers. Give each party a single named owner and agree what will prompt a review, such as a new contract, a new country or a change in the law.
For a project-style walkthrough of putting this in place, see our guide on how to implement clause 4.2.
ISO 27001 made easy
An 81% Headstart from day one
We’ve done the hard work for you, giving you an 81% Headstart from the moment you log on. All you have to do is fill in the blanks.
What kinds of requirements do interested parties have?
Requirements differ in how clear and how binding they are. Sorting them into types helps you see which carry the most weight and which are easy to overlook.
- Legal and regulatory: UK GDPR and the Data Protection Act 2018 for personal data; the Network and Information Systems Regulations 2018 if you are in scope; and, for organisations operating in the EU, laws such as the NIS 2 Directive or, for financial entities, DORA.
- Contractual: security clauses, audit rights, incident reporting terms and service levels agreed with customers, suppliers and partners.
- Industry standards and schemes: certifications or attestations that customers ask for, such as ISO 27001 itself, SOC 2 or PCI DSS.
- Internal: board priorities, risk appetite and internal policies, such as HR rules on handling personal data.
- Implicit expectations: things nobody writes down but parties still expect, such as customers expecting their data to be kept confidential, or concerns about privacy, ESG and the ethical use of AI.
Some requirements are emerging rather than current: a planned move into a new market, an acquisition or a new digital service can bring new parties and new obligations. Recording these early gives the ISMS time to respond.
“Quiet” parties, such as procurement teams, remote branches or a single large customer, can have significant influence even if they rarely raise security directly. Their needs can change without anyone noticing unless someone owns them.
What does an interested parties register look like?
Clause 4.2 does not prescribe a format. A register is a common way to record the parties, their requirements and the decisions you made. The rows below are an illustrative example only; your parties, sources and owners will differ.
| Interested party | Requirement | Source | Linked control or ISMS area | Owner | Review trigger |
|---|---|---|---|---|---|
| Business customers | Protect customer data as agreed in contract | Customer contracts and data processing agreements | Annex A 5.31 Legal, statutory, regulatory and contractual requirements | Head of legal | New or renewed contract |
| UK data protection regulator (Information Commission) | Process personal data lawfully and notify qualifying personal data breaches | UK GDPR (including Article 33) and the Data Protection Act 2018 | Annex A 5.34 Privacy and protection of personal identifiable information (PII); 5.24 incident management planning | Data protection lead | Change in the law or in how you use personal data |
| Employees | Clear security rules and training | Employment contracts and internal policies | Annex A 6.3 Information security awareness, education and training | HR lead | Policy change; new joiners |
| Cloud hosting provider | Customer carries out its share of security responsibilities | Provider terms of service | Annex A 5.23 Information security for use of cloud services | IT manager | Change of provider terms or services |
| Cyber insurer | Security conditions set in the policy, for example backups | Insurance policy wording | Annex A 8.13 Information backup | Finance lead | Policy renewal |
| Board | Information security that supports business strategy and risk appetite | Board minutes and business plan | Clause 5.1 Leadership and commitment; clause 6.1 risk planning | Information security manager | Change of strategy; management review |
An auditor or customer doing due diligence may ask how you arrived at this list. Records that help show your reasoning include:
- a current list of parties, each with a named owner;
- each requirement linked to its source, such as the law, contract or policy;
- dated notes of reviews and changes, with the reason for each addition or removal;
- notes from meetings where legal, IT, operations and senior managers discussed the list;
- a clear link from each addressed requirement to the risks and controls in your ISMS.
Clause 4.2 itself does not require documented information, but clause 7.5.1 requires the documented information your organisation decides is necessary for an effective ISMS, and most organisations choose to keep a register. Keeping it current takes named owners and time, which you plan for under clause 7.1 resources.
How often should you review interested parties?
Clause 4.2 sets no review frequency. A common approach is to review the list at planned intervals that you choose, for example quarterly or ahead of each management review, and also whenever something significant changes. Clause 9.3.2 lists changes in the needs and expectations of interested parties as an input to management review, so the list needs to be current at that point.
Events that often prompt a review include:
- a new customer, supplier or partner contract, or a change to an existing one;
- entering a new country or market, or launching a new service;
- an acquisition, merger or restructure;
- a new or amended law or regulation that applies to you;
- a security incident, or a review after one, that shows a party was missed.
Useful sources for spotting change include updates from the regulators that cover your sector, NCSC guidance, customer feedback and questionnaires, contract amendments and board decisions.
What are the common mistakes with clause 4.2?
- Relying on an old list, or a once-a-year review that misses changes in between
- Recording only written requirements and missing implicit or emerging ones
- Treating the work as a task for legal or IT alone, without input from the board, HR, operations and frontline teams
- Giving a party to “everyone”, so nobody owns it
- Keeping the list in a separate spreadsheet that is never linked to the risk register or controls
Clause 4.2 sets no review frequency. Review at intervals you choose, and whenever a contract, market or law changes.

Manage all your compliance, all in one place
ISMS.online supports over 100 standards and regulations, giving you a single platform for all your compliance needs.
How does clause 4.2 connect to the rest of your ISMS?
Clause 4.2 is an input to several later clauses of ISO/IEC 27001:2022, which is why gaps here tend to show up elsewhere:
- Clause 4.3 (scope): when you set the boundaries of the ISMS, you must consider the requirements identified under clause 4.2.
- Clause 6.1.1 (risks and opportunities): planning must consider the issues from clause 4.1 and the requirements from clause 4.2.
- Annex A 5.31: the control on legal, statutory, regulatory and contractual requirements covers identifying and keeping up to date with these obligations.
- Clause 9.3.2 (management review): changes in the needs and expectations of interested parties are a required input.
If a party is missed, its requirements may never reach the scope, the risk assessment or the controls, and the gap may only surface when a contract term is not met or an incident occurs. Treating clause 4.2 as a living list, rather than a one-off exercise, keeps the rest of the ISMS pointed at the right requirements.
Why choose ISMS.online for clause 4.2?
ISMS.online gives you one place to record your interested parties and their requirements, alongside the rest of your ISMS rather than in an isolated spreadsheet. It helps you:
- Record each interested party, its requirements and where each requirement comes from
- Link requirements to your risks, controls and the scope of your ISMS
- Give each party a named owner and keep a dated history of reviews and changes
- Use workflows and reminders so reviews happen when they should
- Show the trail from party to requirement to control when a customer or auditor asks
ISMS.online is a compliance platform, not a certification body: it helps you prepare for ISO 27001 certification, and certificates are issued by accredited certification bodies. To see how ISMS.online can help you manage interested parties for clause 4.2, book a demo.
Frequently Asked Questions
Is clause 4.2 the same as a stakeholder analysis?
They are closely related. A general stakeholder analysis often covers everyone with an interest in a business or project. Clause 4.2 is narrower: it covers only the parties relevant to your ISMS, and it asks you to go further by recording their requirements and deciding which of them the ISMS will address. An existing stakeholder analysis can be a useful starting point for the clause 4.2 list.
Does clause 4.2 cover climate change?
Yes, as a point to consider. Amendment 1 to the standard (ISO/IEC 27001:2022/Amd 1:2024) added a second note to clause 4.2: the parties relevant to your ISMS may have climate-related requirements. The same amendment added a sentence to clause 4.1 asking you to decide whether climate change is a relevant issue for you. Whether it matters for your ISMS is your decision, and recording that decision shows you considered it.
Which interested parties are easiest to miss?
The parties that rarely raise security themselves. Common examples are:
- niche suppliers or software tools that project teams bring in without a central review;
- contractors working overseas, and overseas sales subsidiaries with their own local obligations;
- vendors that can push code or changes straight into production;
- operational teams, such as procurement, logistics or field service, that work across legal or industry boundaries.
Linking reviews to supplier onboarding, project launches and new hires helps these parties surface early.
Do you have to address every requirement an interested party has?
No. Point c) of clause 4.2 asks you to determine which of the relevant requirements will be addressed through the ISMS, so some may sit outside it, for example because another management system or business process handles them. Legal and contractual obligations still apply to the organisation whether or not the ISMS covers them, so record where each one is handled and why.
How can you make clause 4.2 part of everyday work?
Build the review into processes that already exist rather than saving it for audit season. Practical steps include:
- adding a “new interested party or requirement?” question to contract, project and supplier approval checklists;
- training managers and frontline staff to flag “not sure if this matters” moments to the register owner;
- including a check for missed parties in reviews after security incidents.