















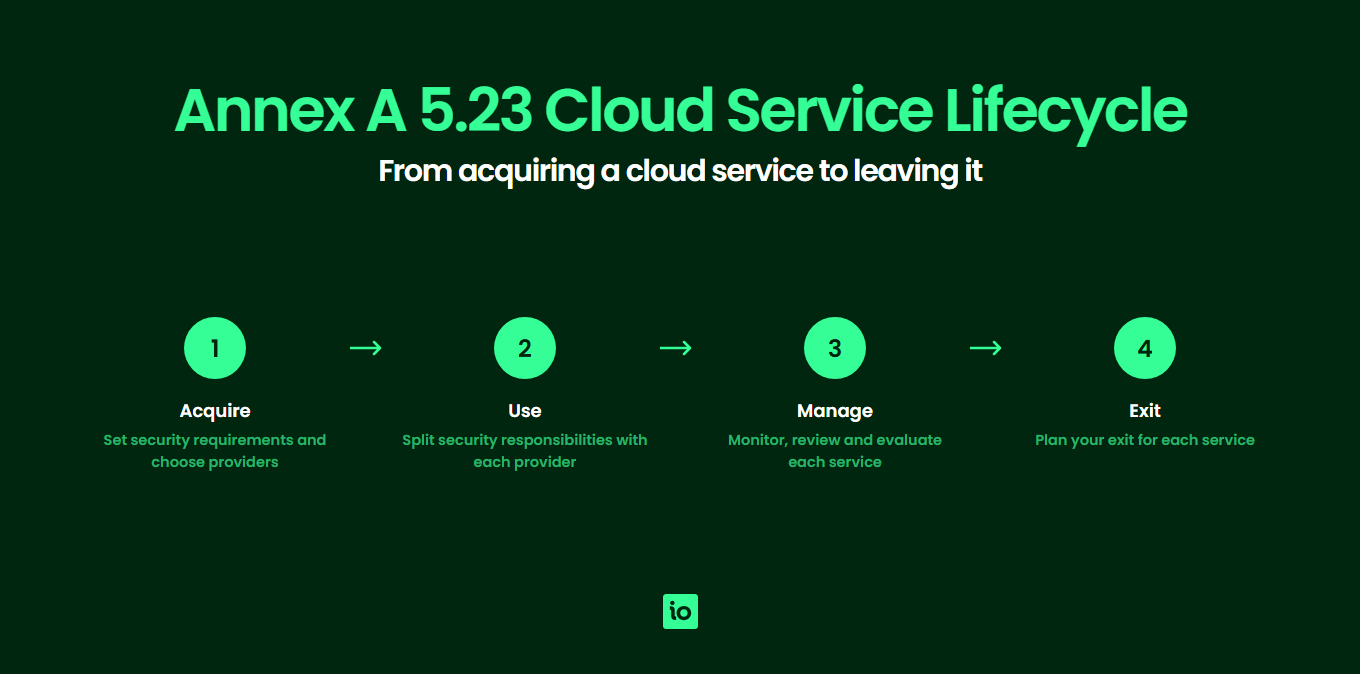
ISO 27001:2022 Annex A 5.23, Information security for use of cloud services, requires an organisation to set up processes for acquiring, using, managing and leaving cloud services in line with its own information security requirements. The control treats the organisation as the cloud service customer and covers policy, provider choice, shared responsibilities, agreements and exit plans.
Can You Use Cloud Services and Still Achieve ISO 27001 Certification?
Yes. ISO 27001:2022 does not ask you to avoid cloud services; it asks you to manage them. Certificates are issued by accredited certification bodies after an audit of your management system, not by the cloud provider or by software vendors.
Like every Annex A control, 5.23 is recorded in your Statement of Applicability, which lists the controls you need, why you include them, whether they are implemented and why any Annex A control is excluded (ISO 27001:2022 clause 6.1.3 d). For a managed service provider’s view of the same question, see our guide to using public cloud platforms while staying ISO 27001 compliant.
What Is ISO 27001:2022 Annex A 5.23?
ISO 27001:2022 Annex A 5.23 is a new control with no equivalent in ISO 27001:2013. Its purpose is to let an organisation specify and manage information security concepts for the cloud services it uses, in its capacity as a “cloud service customer”.
ISO/IEC 27002:2022 classes 5.23 as a preventive control that supports confidentiality, integrity and availability. It is put into practice through policies and procedures that govern information security for the cloud services the organisation uses.
Who Owns Annex A 5.23?
Cloud services now support many parts of a business, so ISO 27001 2022 Annex A Control 5.23 reaches well beyond the IT team.
ISO/IEC 27002:2022 does not name a job title for this control. Your organisation decides who owns it and records that decision, often giving it to a senior IT, security or operations lead. Because the control also asks you to define roles and responsibilities for using and managing cloud services, the owner usually works with procurement, legal and the teams that buy cloud tools.
What Must an Organisation Define Under Annex A 5.23?
ISO/IEC 27002:2022 asks for a topic-specific policy on the use of cloud services, communicated to everyone it affects. This sits alongside your main information security policy and covers cloud use as a subject in its own right.
The guidance also says you should define and communicate how you will manage the information security risks of using cloud services. This can extend the approach you already use for other external suppliers, so 5.23 should be aligned with Controls 5.21 (managing information security in the ICT supply chain) and 5.22 (monitoring, review and change management of supplier services). Read the ISO 27002 control 5.23 guidance for the supporting detail.
ISO/IEC 27002:2022 says using cloud services can involve shared work: responsibility can be split between the provider and the organisation, and both sides need to cooperate. With that in mind, the organisation should define:
- All relevant information security requirements involved in using a cloud service.
- The criteria for selecting a cloud service provider, and the scope of how its services will be used.
- The roles and responsibilities that govern how cloud services are to be used and managed across the organisation.
- Precisely which security controls the cloud provider runs, and which the organisation runs itself.
- How to obtain and use any information security features provided by the cloud service.
- How to obtain assurance on the information security controls run by the cloud service provider.
- How to manage controls, interfaces and changes when using several cloud services, particularly from different providers.
- Incident Management procedures for security incidents linked to the use of cloud services.
- How the organisation will monitor, review and evaluate its cloud services over time to keep the related security risks under control.
- How to change or stop using cloud services, including an exit strategy for each one.
ISO 27001 made easy
An 81% Headstart from day one
We’ve done the hard work for you, giving you an 81% Headstart from the moment you log on. All you have to do is fill in the blanks.
How Do You Split Security Responsibilities With a Cloud Provider?
Item 4 above deserves its own record, because the split differs from one cloud service to another. Write it down for each provider rather than assume it. The table below shows areas to settle and record; it is a starting point, not a fixed split.
| Area to settle | What to agree or check with the provider | What stays with your organisation |
|---|---|---|
| Access | How the service’s access controls can meet your requirements | Who gets accounts and permissions, and removing them when people leave |
| Malware and monitoring | What malware monitoring and protection the service provides | Protecting your own devices and the data your users upload |
| Data location | Which countries, regions or jurisdictions your data is stored and processed in | Deciding which locations are acceptable for your information |
| Backups | What backup of data and configuration the provider offers | Checking those backups meet your needs, and adding your own where they do not |
| Incidents | What support the provider gives during a security incident in the service | Your own incident procedures for cloud-related incidents |
| Exit | Support during exit, and return of your data, configuration files and code | Your exit plan and where the service will move to |
Worked example: suppose a company moves its customer records into a cloud CRM tool. The provider runs the hosting and the platform’s security features. The company still decides who can see which records, removes access when staff leave, checks which region the data is held in and keeps a plan for exporting the records if it changes supplier.
What Should a Cloud Services Agreement Cover Under Annex A 5.23?
ISO/IEC 27002:2022 recognises that cloud service agreements are often fixed in advance, with little room to negotiate. You should still review every cloud service agreement and check that it addresses four of your requirements:
- Confidentiality.
- Integrity.
- Availability.
- Information handling.
Carry out relevant risk assessments to identify the risks of using the cloud service. Any risk left over from using the service should be clearly identified and accepted by the right level of management.
Use the 10 provisions below as a checklist. ISO/IEC 27002:2022 says an agreement between the organisation and the cloud service provider should include provisions on:
- Recognised standards: the service is built on industry-accepted standards for cloud architecture and hosted infrastructure.
- Access control: access to the cloud service is managed so that it meets the organisation’s requirements.
- Malware protection: malware monitoring and protection are in place.
- Data location: sensitive information is processed and stored only in approved locations, such as a named country or region, or under a set jurisdiction.
- Incident support: the provider gives dedicated support if an information security incident happens in the cloud service.
- Sub-contracting: the organisation’s information security requirements still apply if any part of the service is sub-contracted, or sub-contracting is ruled out altogether.
- Digital evidence: the provider helps the organisation gather digital evidence, taking account of the laws on evidence in different jurisdictions.
- Exit support: the provider offers suitable support and service availability for a reasonable period when the organisation leaves the service.
- Backups: the provider backs up data and configuration information and manages those backups securely, where its service allows.
- Return of information: the provider returns configuration files, source code and data the organisation owns, when asked during the contract or when it ends.

Manage all your compliance, all in one place
ISMS.online supports over 100 standards and regulations, giving you a single platform for all your compliance needs.
What Changes Should a Cloud Provider Tell You About?
ISO/IEC 27002:2022 also advises organisations to keep in close contact with their cloud service providers, so both sides can share information security updates and report any failure to meet what the agreement promises.
Consider whether the agreement should require the provider to give advance notice before any significant change to how the service is delivered, including:
- Changes to technical infrastructure, such as relocation, reconfiguration or new hardware or software, that affect the service.
- Processing or storing information in a new geographical region or legal jurisdiction.
- Using “peer cloud” providers or other sub-contractors, including new or changed parties.
What Evidence Shows Annex A 5.23 Is in Place?
An auditor or a customer doing due diligence may ask to see records such as:
- Your topic-specific policy on the use of cloud services, and how it was communicated.
- Selection criteria and due-diligence records for each cloud provider.
- The recorded split of security responsibilities for each service.
- Reviews of each cloud service agreement against your requirements, with the risk assessment and any accepted leftover risk.
- Records of monitoring and reviewing your cloud services over time.
- An exit plan for each important cloud service.
For step-by-step help putting these in place, see our guide on how to implement Annex A 5.23.
Supporting Annex A Controls
- ISO 27001:2022 Annex A 5.21
- ISO 27001:2022 Annex A 5.22
What Are the Changes and Differences From ISO 27001:2013?
ISO/IEC 27002:2022 lists control 5.23 as new in its table mapping the 2022 controls to the 2013 edition.
What Are All the ISO 27001:2022 Annex A Controls?
In the table below you’ll find more information on each individual ISO 27001:2022 Annex A Control.
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Organisational Controls | Annex A 5.1 |
Annex A 5.1.1 Annex A 5.1.2 |
Policies for Information Security |
| Organisational Controls | Annex A 5.2 | Annex A 6.1.1 | Information Security Roles and Responsibilities |
| Organisational Controls | Annex A 5.3 | Annex A 6.1.2 | Segregation of Duties |
| Organisational Controls | Annex A 5.4 | Annex A 7.2.1 | Management Responsibilities |
| Organisational Controls | Annex A 5.5 | Annex A 6.1.3 | Contact With Authorities |
| Organisational Controls | Annex A 5.6 | Annex A 6.1.4 | Contact With Special Interest Groups |
| Organisational Controls | Annex A 5.7 | NEW | Threat Intelligence |
| Organisational Controls | Annex A 5.8 |
Annex A 6.1.5 Annex A 14.1.1 |
Information Security in Project Management |
| Organisational Controls | Annex A 5.9 |
Annex A 8.1.1 Annex A 8.1.2 |
Inventory of Information and Other Associated Assets |
| Organisational Controls | Annex A 5.10 |
Annex A 8.1.3 Annex A 8.2.3 |
Acceptable Use of Information and Other Associated Assets |
| Organisational Controls | Annex A 5.11 | Annex A 8.1.4 | Return of Assets |
| Organisational Controls | Annex A 5.12 | Annex A 8.2.1 | Classification of Information |
| Organisational Controls | Annex A 5.13 | Annex A 8.2.2 | Labelling of Information |
| Organisational Controls | Annex A 5.14 |
Annex A 13.2.1 Annex A 13.2.2 Annex A 13.2.3 |
Information Transfer |
| Organisational Controls | Annex A 5.15 |
Annex A 9.1.1 Annex A 9.1.2 |
Access Control |
| Organisational Controls | Annex A 5.16 | Annex A 9.2.1 | Identity Management |
| Organisational Controls | Annex A 5.17 |
Annex A 9.2.4 Annex A 9.3.1 Annex A 9.4.3 |
Authentication Information |
| Organisational Controls | Annex A 5.18 |
Annex A 9.2.2 Annex A 9.2.5 Annex A 9.2.6 |
Access Rights |
| Organisational Controls | Annex A 5.19 | Annex A 15.1.1 | Information Security in Supplier Relationships |
| Organisational Controls | Annex A 5.20 | Annex A 15.1.2 | Addressing Information Security Within Supplier Agreements |
| Organisational Controls | Annex A 5.21 | Annex A 15.1.3 | Managing Information Security in the ICT Supply Chain |
| Organisational Controls | Annex A 5.22 |
Annex A 15.2.1 Annex A 15.2.2 |
Monitoring, Review and Change Management of Supplier Services |
| Organisational Controls | Annex A 5.23 | NEW | Information Security for Use of Cloud Services |
| Organisational Controls | Annex A 5.24 | Annex A 16.1.1 | Information Security Incident Management Planning and Preparation |
| Organisational Controls | Annex A 5.25 | Annex A 16.1.4 | Assessment and Decision on Information Security Events |
| Organisational Controls | Annex A 5.26 | Annex A 16.1.5 | Response to Information Security Incidents |
| Organisational Controls | Annex A 5.27 | Annex A 16.1.6 | Learning From Information Security Incidents |
| Organisational Controls | Annex A 5.28 | Annex A 16.1.7 | Collection of Evidence |
| Organisational Controls | Annex A 5.29 |
Annex A 17.1.1 Annex A 17.1.2 Annex A 17.1.3 |
Information Security During Disruption |
| Organisational Controls | Annex A 5.30 | NEW | ICT Readiness for Business Continuity |
| Organisational Controls | Annex A 5.31 |
Annex A 18.1.1 Annex A 18.1.5 |
Legal, Statutory, Regulatory and Contractual Requirements |
| Organisational Controls | Annex A 5.32 | Annex A 18.1.2 | Intellectual Property Rights |
| Organisational Controls | Annex A 5.33 | Annex A 18.1.3 | Protection of Records |
| Organisational Controls | Annex A 5.34 | Annex A 18.1.4 | Privacy and Protection of PII |
| Organisational Controls | Annex A 5.35 | Annex A 18.2.1 | Independent Review of Information Security |
| Organisational Controls | Annex A 5.36 |
Annex A 18.2.2 Annex A 18.2.3 |
Compliance With Policies, Rules and Standards for Information Security |
| Organisational Controls | Annex A 5.37 | Annex A 12.1.1 | Documented Operating Procedures |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| People Controls | Annex A 6.1 | Annex A 7.1.1 | Screening |
| People Controls | Annex A 6.2 | Annex A 7.1.2 | Terms and Conditions of Employment |
| People Controls | Annex A 6.3 | Annex A 7.2.2 | Information Security Awareness, Education and Training |
| People Controls | Annex A 6.4 | Annex A 7.2.3 | Disciplinary Process |
| People Controls | Annex A 6.5 | Annex A 7.3.1 | Responsibilities After Termination or Change of Employment |
| People Controls | Annex A 6.6 | Annex A 13.2.4 | Confidentiality or Non-Disclosure Agreements |
| People Controls | Annex A 6.7 | Annex A 6.2.2 | Remote Working |
| People Controls | Annex A 6.8 |
Annex A 16.1.2 Annex A 16.1.3 |
Information Security Event Reporting |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Physical Controls | Annex A 7.1 | Annex A 11.1.1 | Physical Security Perimeters |
| Physical Controls | Annex A 7.2 |
Annex A 11.1.2 Annex A 11.1.6 |
Physical Entry |
| Physical Controls | Annex A 7.3 | Annex A 11.1.3 | Securing Offices, Rooms and Facilities |
| Physical Controls | Annex A 7.4 | NEW | Physical Security Monitoring |
| Physical Controls | Annex A 7.5 | Annex A 11.1.4 | Protecting Against Physical and Environmental Threats |
| Physical Controls | Annex A 7.6 | Annex A 11.1.5 | Working In Secure Areas |
| Physical Controls | Annex A 7.7 | Annex A 11.2.9 | Clear Desk and Clear Screen |
| Physical Controls | Annex A 7.8 | Annex A 11.2.1 | Equipment Siting and Protection |
| Physical Controls | Annex A 7.9 | Annex A 11.2.6 | Security of Assets Off-Premises |
| Physical Controls | Annex A 7.10 |
Annex A 8.3.1 Annex A 8.3.2 Annex A 8.3.3 Annex A 11.2.5 |
Storage Media |
| Physical Controls | Annex A 7.11 | Annex A 11.2.2 | Supporting Utilities |
| Physical Controls | Annex A 7.12 | Annex A 11.2.3 | Cabling Security |
| Physical Controls | Annex A 7.13 | Annex A 11.2.4 | Equipment Maintenance |
| Physical Controls | Annex A 7.14 | Annex A 11.2.7 | Secure Disposal or Re-Use of Equipment |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Technological Controls | Annex A 8.1 |
Annex A 6.2.1 Annex A 11.2.8 |
User Endpoint Devices |
| Technological Controls | Annex A 8.2 | Annex A 9.2.3 | Privileged Access Rights |
| Technological Controls | Annex A 8.3 | Annex A 9.4.1 | Information Access Restriction |
| Technological Controls | Annex A 8.4 | Annex A 9.4.5 | Access to Source Code |
| Technological Controls | Annex A 8.5 | Annex A 9.4.2 | Secure Authentication |
| Technological Controls | Annex A 8.6 | Annex A 12.1.3 | Capacity Management |
| Technological Controls | Annex A 8.7 | Annex A 12.2.1 | Protection Against Malware |
| Technological Controls | Annex A 8.8 |
Annex A 12.6.1 Annex A 18.2.3 |
Management of Technical Vulnerabilities |
| Technological Controls | Annex A 8.9 | NEW | Configuration Management |
| Technological Controls | Annex A 8.10 | NEW | Information Deletion |
| Technological Controls | Annex A 8.11 | NEW | Data Masking |
| Technological Controls | Annex A 8.12 | NEW | Data Leakage Prevention |
| Technological Controls | Annex A 8.13 | Annex A 12.3.1 | Information Backup |
| Technological Controls | Annex A 8.14 | Annex A 17.2.1 | Redundancy of Information Processing Facilities |
| Technological Controls | Annex A 8.15 |
Annex A 12.4.1 Annex A 12.4.2 Annex A 12.4.3 |
Logging |
| Technological Controls | Annex A 8.16 | NEW | Monitoring Activities |
| Technological Controls | Annex A 8.17 | Annex A 12.4.4 | Clock Synchronization |
| Technological Controls | Annex A 8.18 | Annex A 9.4.4 | Use of Privileged Utility ProgramsAccess Rights |
| Technological Controls | Annex A 8.19 |
Annex A 12.5.1 Annex A 12.6.2 |
Installation of Software on Operational Systems |
| Technological Controls | Annex A 8.20 | Annex A 13.1.1 | Networks Security |
| Technological Controls | Annex A 8.21 | Annex A 13.1.2 | Security of Network Services |
| Technological Controls | Annex A 8.22 | Annex A 13.1.3 | Segregation of Networks |
| Technological Controls | Annex A 8.23 | NEW | Web filtering |
| Technological Controls | Annex A 8.24 |
Annex A 10.1.1 Annex A 10.1.2 |
Use of Cryptography |
| Technological Controls | Annex A 8.25 | Annex A 14.2.1 | Secure Development Life Cycle |
| Technological Controls | Annex A 8.26 |
Annex A 14.1.2 Annex A 14.1.3 |
Application Security Requirements |
| Technological Controls | Annex A 8.27 | Annex A 14.2.5 | Secure System Architecture and Engineering PrinciplesLearning From Information Security Incidents |
| Technological Controls | Annex A 8.28 | NEW | Secure Coding |
| Technological Controls | Annex A 8.29 |
Annex A 14.2.8 Annex A 14.2.9 |
Security Testing in Development and Acceptance |
| Technological Controls | Annex A 8.30 | Annex A 14.2.7 | Outsourced Development |
| Technological Controls | Annex A 8.31 |
Annex A 12.1.4 Annex A 14.2.6 |
Separation of Development, Test and Production Environments |
| Technological Controls | Annex A 8.32 |
Annex A 12.1.2 Annex A 14.2.2 Annex A 14.2.3 Annex A 14.2.4 |
Change Management |
| Technological Controls | Annex A 8.33 | Annex A 14.3.1 | Test Information |
| Technological Controls | Annex A 8.34 | Annex A 12.7.1 | Protection of Information Systems During Audit Testing |
Why Choose ISMS.online for Annex A 5.23?
ISMS.online gives you a cloud-based framework for documenting your information security management system, including the procedures and checklists behind controls such as Annex A 5.23. It helps you:
- Streamline your ISO 27001 implementation.
- Build an ISMS that is compatible with ISO 27001.
- Document your information security procedures and checklists.
- Allocate tasks and track progress towards compliance.
- Complete tasks and record proof that they meet the requirements of the standard.
- Get help from a specialist team of advisers throughout your path to compliance.
To see how ISMS.online can help you manage your cloud services under ISO 27001, book a demo.
FAQs
Is Annex A 5.23 the same as ISO 27002 control 5.23?
They share a number and a title but do different jobs. Annex A 5.23 in ISO 27001:2022 is the control you address in your management system and record in your Statement of Applicability. ISO/IEC 27002:2022 control 5.23 gives the supporting guidance on putting it into practice, such as the topic-specific policy, the points to define and the agreement provisions.
Does Annex A 5.23 cover cloud services you provide to your own customers?
No. Annex A 5.23 treats your organisation as the cloud service customer. It covers the cloud services you acquire, use, manage and leave, not how you run a cloud service for others.
Does a cloud provider’s own certificate cover your use of its service?
No. A certificate follows an audit of a management system, so a provider’s certificate relates to the provider’s own system, not yours. Under Annex A 5.23 you still decide how to obtain assurance on the controls the provider runs, and record which controls stay with your organisation.

NHS Professionals achieves ISO 27001 certification and improves their infosec management
Facing a tight six-month deadline and multiple existing frameworks to integrate, NHS Professionals needed a platform that could incorporate ISO 27001 without duplicating policies or adding risk to their already complex compliance landscape.
Xergy tool Proteus generates growth through ISO 27001 compliance using ISMS.online
As a start-up building software for highly regulated engineering sectors, Xergy needed ISO 27001 to generate growth through trust — and a proven external partner to handle the rigorous requirements without diverting the dev team.
How MAAS Aviation Built a Robust and Sustainable ISO 27001-Compliant ISMS
MAAS Aviation required strong technical foundations to support ISO 27001 alignment, and a platform to centralise compliance management.
How Blue Services Achieved Triple ISO Certification Success
Blue Services needed external support to guide them through ISO 27001, ISO 9001 and ISO 14001 implementation and best practices, and a platform to centralise their overall compliance management.
How Evolution Funding Cruised to ISO 27001 Certification Success
Achieving ISO 27001 certification was a core objective for Evolution Funding. The team needed a centralised platform with which they could implement the ISO 27001 standard and work through the compliance process.
How 4way Consulting Paved the Road to ISO 27001 Success
Handling sensitive client data across multiple standards, 4way needed a cost and time-efficient way to pursue ISO 27001 – without building an ISMS from scratch or relying on expensive external consultants.