








ISO 27001:2022 Annex A 5.34, Privacy and protection of PII, is a preventive control that requires an organisation to work out which privacy and personal data protection requirements apply to it under laws, regulations and contracts, and then meet them. PII (personally identifiable information) is any information that can identify a person, directly or indirectly.
What counts as PII under Annex A 5.34?
ISO 27002:2022 treats PII as any information that can be linked, directly or indirectly, to the person it relates to. UK GDPR uses the term personal data and gives examples of identifiers such as a name, an identification number, location data and an online identifier (UK GDPR Article 4(1)).
Examples of PII a UK organisation is likely to hold include:
- Names, home addresses and personal email addresses.
- National Insurance numbers.
- NHS numbers and medical records.
- Driving licence numbers.
- Bank account and other financial details.
Health information, such as medical records, is special category data under UK GDPR Article 9, which sets stricter conditions for processing it.
PII brings its own legal, regulatory and contractual risks. Annex A 5.34 covers two linked aims: preserving people’s privacy and protecting the PII the organisation holds.
What is the purpose of Annex A 5.34?
ISO 27002:2022 describes its purpose as making sure the organisation complies with the legal, statutory, regulatory and contractual requirements that cover the information security side of protecting PII.
The organisation meets it through a policy and procedures written for its own obligations and the PII it handles. For detailed guidance, see the ISO 27002 control 5.34 guidance.
Who owns Annex A 5.34?
ISO 27002:2022 does not set a fixed owner. Its guidance says that meeting the control usually works best when one person is made responsible, such as a privacy officer. That person advises staff, suppliers and other interested parties about their individual duties and the procedures to follow.
A privacy officer is not the same as a data protection officer (DPO). UK GDPR Article 37 requires a DPO only in set cases: public authorities and bodies (except courts and tribunals acting in their judicial capacity), and organisations whose core activities involve large-scale regular and systematic monitoring of people, or large-scale processing of special category data or data about criminal convictions and offences. Where a DPO exists, they can take on the privacy officer duties too; Annex A 5.34 does not require a DPO.
ISO 27001 made easy
An 81% Headstart from day one
We’ve done the hard work for you, giving you an 81% Headstart from the moment you log on. All you have to do is fill in the blanks.
How do you implement Annex A 5.34?
ISO 27002:2022 sets out the main steps:
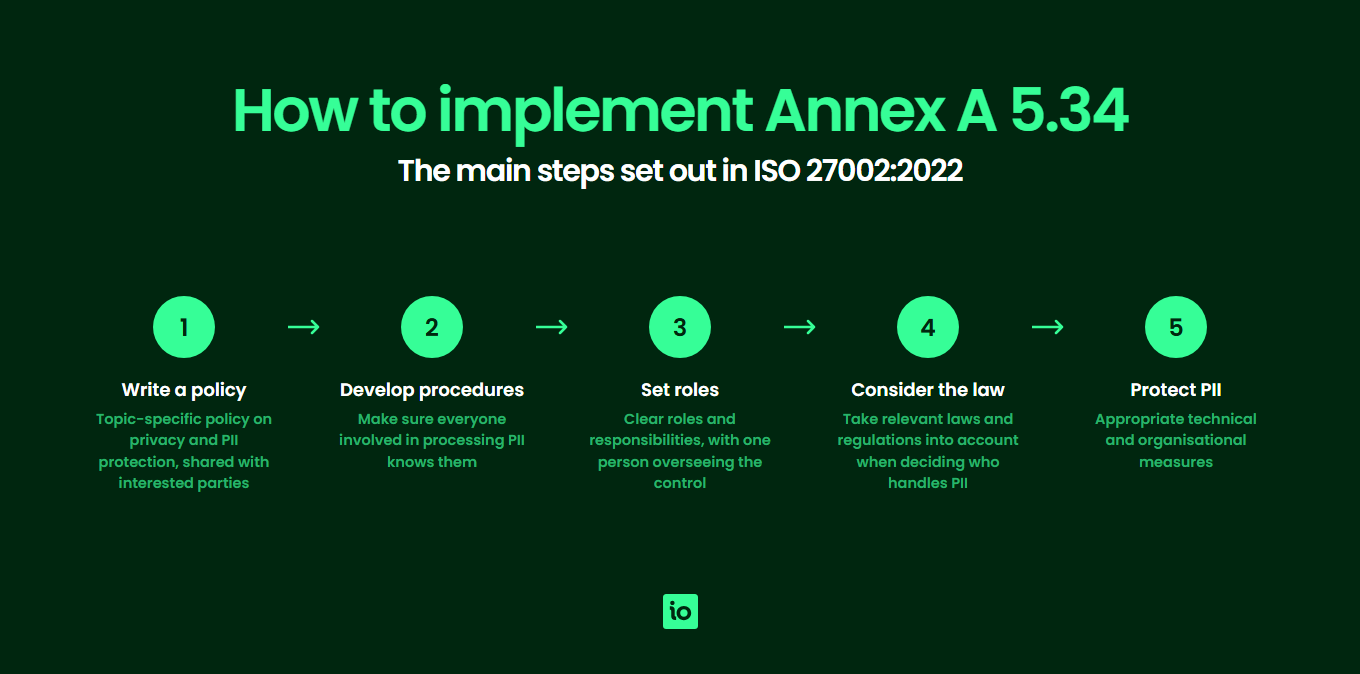
- Write a topic-specific policy covering privacy and PII protection, and share it with all relevant interested parties.
- Develop procedures for preserving privacy and protecting PII, and make sure everyone involved in processing PII knows them.
- Set clear roles and responsibilities, with one person overseeing the control (see above).
- Take relevant laws and regulations into account when deciding who handles PII and how.
- Put appropriate technical and organisational measures in place to protect PII.
Write the policy for the PII your organisation handles most often rather than using a generic template, and lead it from the top so roles and data controls stay consistent. For a step-by-step approach, see how to implement Annex A 5.34.
Example: what a PII register can record
A register of the PII you hold is a practical starting point. The fields below draw on the record of processing activities in UK GDPR Article 30, plus a legal basis and an owner. The example entries are illustrative.
| Field | What to record | Example entry |
|---|---|---|
| Type of PII | The category of personal data | Employee bank details |
| People it relates to | Whose data it is | Current employees |
| Purpose | Why you hold and use it | Paying salaries |
| Legal basis | Your lawful basis for processing under UK GDPR Article 6 | Performance of the employment contract |
| Owner | The person accountable for this data | Head of HR |
| Storage and recipients | Where it is held and who it is shared with | HR system; payroll provider |
| Retention | How long you keep it and how it is deleted | The period set in your retention schedule |
| Security measures | The controls that protect it | Role-based access and encryption |
Does ISO 27001 cover data privacy and GDPR?
Partly. ISO 27001:2022 is a standard for an information security management system (ISMS), not a privacy law. Annex A 5.34 brings privacy into the ISMS by requiring the organisation to identify and meet the privacy and PII protection requirements that apply to it. For organisations in the UK, those requirements include UK GDPR and the Data Protection Act 2018, along with any contract terms about personal data.
The two overlap most on security. UK GDPR Article 32 requires controllers and processors to put in place technical and organisational measures that give a level of security appropriate to the risk. An ISO 27001 ISMS is one structured way to choose, run and review those measures. For privacy management beyond security, see ISO/IEC 27701 in the table below.
Which other ISO standards cover PII protection?
Privacy laws differ between countries. ISO 27002:2022 notes that national laws can place duties on organisations that collect, process and share PII, and can restrict transfers of PII abroad, so review the effect of handling personal information across borders. ISO 27001:2022 does not explain how to meet these laws; ISO 27002:2022 points to three other standards:
| Standard | What it is | Who it is for | How it relates to ISO 27001 |
|---|---|---|---|
| ISO/IEC 29100 | A high-level privacy framework for protecting PII in information and communications technology (ICT) systems | Organisations designing or running systems that process PII | Background framework; ISO 27002:2022 takes several of its PII terms from it |
| ISO/IEC 27701 | Requirements and guidance for a privacy information management system (PIMS) | Organisations that process PII, as controllers or processors | The 2019 edition was an extension to ISO 27001 and ISO 27002; the 2025 edition is a stand-alone standard that can be integrated with an ISO 27001 ISMS |
| ISO/IEC 27018 | A code of practice for protecting PII in public clouds | Public cloud providers acting as PII processors | ISO 27002:2022 points to it for privacy in public cloud services |

Free yourself from a mountain of spreadsheets
Embed, expand and scale your compliance, without the mess. IO gives you the resilience and confidence to grow securely.
What changed from ISO 27001:2013?
Annex A 5.34 replaces ISO 27001:2013 Annex A 18.1.4 (Privacy and protection of personally identifiable information) in the 2022 update to ISO 27001. The subject of the control is the same; the differences are in what it asks for:
- The 2013 control asked for privacy and PII protection to be ensured where relevant laws and regulations required it. The 2022 control asks the organisation to identify and meet the requirements, and adds contractual requirements alongside laws and regulations.
- ISO 27002:2022 guidance asks for a topic-specific policy on privacy and PII protection, shared with all relevant interested parties.
Where can you find all the ISO 27001:2022 Annex A controls?
In the table below you’ll find more information on each individual ISO 27001:2022 Annex A Control.
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Organisational Controls | Annex A 5.1 |
Annex A 5.1.1 Annex A 5.1.2 |
Policies for Information Security |
| Organisational Controls | Annex A 5.2 | Annex A 6.1.1 | Information Security Roles and Responsibilities |
| Organisational Controls | Annex A 5.3 | Annex A 6.1.2 | Segregation of Duties |
| Organisational Controls | Annex A 5.4 | Annex A 7.2.1 | Management Responsibilities |
| Organisational Controls | Annex A 5.5 | Annex A 6.1.3 | Contact With Authorities |
| Organisational Controls | Annex A 5.6 | Annex A 6.1.4 | Contact With Special Interest Groups |
| Organisational Controls | Annex A 5.7 | NEW | Threat Intelligence |
| Organisational Controls | Annex A 5.8 |
Annex A 6.1.5 Annex A 14.1.1 |
Information Security in Project Management |
| Organisational Controls | Annex A 5.9 |
Annex A 8.1.1 Annex A 8.1.2 |
Inventory of Information and Other Associated Assets |
| Organisational Controls | Annex A 5.10 |
Annex A 8.1.3 Annex A 8.2.3 |
Acceptable Use of Information and Other Associated Assets |
| Organisational Controls | Annex A 5.11 | Annex A 8.1.4 | Return of Assets |
| Organisational Controls | Annex A 5.12 | Annex A 8.2.1 | Classification of Information |
| Organisational Controls | Annex A 5.13 | Annex A 8.2.2 | Labelling of Information |
| Organisational Controls | Annex A 5.14 |
Annex A 13.2.1 Annex A 13.2.2 Annex A 13.2.3 |
Information Transfer |
| Organisational Controls | Annex A 5.15 |
Annex A 9.1.1 Annex A 9.1.2 |
Access Control |
| Organisational Controls | Annex A 5.16 | Annex A 9.2.1 | Identity Management |
| Organisational Controls | Annex A 5.17 |
Annex A 9.2.4 Annex A 9.3.1 Annex A 9.4.3 |
Authentication Information |
| Organisational Controls | Annex A 5.18 |
Annex A 9.2.2 Annex A 9.2.5 Annex A 9.2.6 |
Access Rights |
| Organisational Controls | Annex A 5.19 | Annex A 15.1.1 | Information Security in Supplier Relationships |
| Organisational Controls | Annex A 5.20 | Annex A 15.1.2 | Addressing Information Security Within Supplier Agreements |
| Organisational Controls | Annex A 5.21 | Annex A 15.1.3 | Managing Information Security in the ICT Supply Chain |
| Organisational Controls | Annex A 5.22 |
Annex A 15.2.1 Annex A 15.2.2 |
Monitoring, Review and Change Management of Supplier Services |
| Organisational Controls | Annex A 5.23 | NEW | Information Security for Use of Cloud Services |
| Organisational Controls | Annex A 5.24 | Annex A 16.1.1 | Information Security Incident Management Planning and Preparation |
| Organisational Controls | Annex A 5.25 | Annex A 16.1.4 | Assessment and Decision on Information Security Events |
| Organisational Controls | Annex A 5.26 | Annex A 16.1.5 | Response to Information Security Incidents |
| Organisational Controls | Annex A 5.27 | Annex A 16.1.6 | Learning From Information Security Incidents |
| Organisational Controls | Annex A 5.28 | Annex A 16.1.7 | Collection of Evidence |
| Organisational Controls | Annex A 5.29 |
Annex A 17.1.1 Annex A 17.1.2 Annex A 17.1.3 |
Information Security During Disruption |
| Organisational Controls | Annex A 5.30 | NEW | ICT Readiness for Business Continuity |
| Organisational Controls | Annex A 5.31 |
Annex A 18.1.1 Annex A 18.1.5 |
Legal, Statutory, Regulatory and Contractual Requirements |
| Organisational Controls | Annex A 5.32 | Annex A 18.1.2 | Intellectual Property Rights |
| Organisational Controls | Annex A 5.33 | Annex A 18.1.3 | Protection of Records |
| Organisational Controls | Annex A 5.34 | Annex A 18.1.4 | Privacy and Protection of PII |
| Organisational Controls | Annex A 5.35 | Annex A 18.2.1 | Independent Review of Information Security |
| Organisational Controls | Annex A 5.36 |
Annex A 18.2.2 Annex A 18.2.3 |
Compliance With Policies, Rules and Standards for Information Security |
| Organisational Controls | Annex A 5.37 | Annex A 12.1.1 | Documented Operating Procedures |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| People Controls | Annex A 6.1 | Annex A 7.1.1 | Screening |
| People Controls | Annex A 6.2 | Annex A 7.1.2 | Terms and Conditions of Employment |
| People Controls | Annex A 6.3 | Annex A 7.2.2 | Information Security Awareness, Education and Training |
| People Controls | Annex A 6.4 | Annex A 7.2.3 | Disciplinary Process |
| People Controls | Annex A 6.5 | Annex A 7.3.1 | Responsibilities After Termination or Change of Employment |
| People Controls | Annex A 6.6 | Annex A 13.2.4 | Confidentiality or Non-Disclosure Agreements |
| People Controls | Annex A 6.7 | Annex A 6.2.2 | Remote Working |
| People Controls | Annex A 6.8 |
Annex A 16.1.2 Annex A 16.1.3 |
Information Security Event Reporting |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Physical Controls | Annex A 7.1 | Annex A 11.1.1 | Physical Security Perimeters |
| Physical Controls | Annex A 7.2 |
Annex A 11.1.2 Annex A 11.1.6 |
Physical Entry |
| Physical Controls | Annex A 7.3 | Annex A 11.1.3 | Securing Offices, Rooms and Facilities |
| Physical Controls | Annex A 7.4 | NEW | Physical Security Monitoring |
| Physical Controls | Annex A 7.5 | Annex A 11.1.4 | Protecting Against Physical and Environmental Threats |
| Physical Controls | Annex A 7.6 | Annex A 11.1.5 | Working In Secure Areas |
| Physical Controls | Annex A 7.7 | Annex A 11.2.9 | Clear Desk and Clear Screen |
| Physical Controls | Annex A 7.8 | Annex A 11.2.1 | Equipment Siting and Protection |
| Physical Controls | Annex A 7.9 | Annex A 11.2.6 | Security of Assets Off-Premises |
| Physical Controls | Annex A 7.10 |
Annex A 8.3.1 Annex A 8.3.2 Annex A 8.3.3 Annex A 11.2.5 |
Storage Media |
| Physical Controls | Annex A 7.11 | Annex A 11.2.2 | Supporting Utilities |
| Physical Controls | Annex A 7.12 | Annex A 11.2.3 | Cabling Security |
| Physical Controls | Annex A 7.13 | Annex A 11.2.4 | Equipment Maintenance |
| Physical Controls | Annex A 7.14 | Annex A 11.2.7 | Secure Disposal or Re-Use of Equipment |
| Annex A Control Type | ISO/IEC 27001:2022 Annex A Identifier | ISO/IEC 27001:2013 Annex A Identifier | Annex A Name |
|---|---|---|---|
| Technological Controls | Annex A 8.1 |
Annex A 6.2.1 Annex A 11.2.8 |
User Endpoint Devices |
| Technological Controls | Annex A 8.2 | Annex A 9.2.3 | Privileged Access Rights |
| Technological Controls | Annex A 8.3 | Annex A 9.4.1 | Information Access Restriction |
| Technological Controls | Annex A 8.4 | Annex A 9.4.5 | Access to Source Code |
| Technological Controls | Annex A 8.5 | Annex A 9.4.2 | Secure Authentication |
| Technological Controls | Annex A 8.6 | Annex A 12.1.3 | Capacity Management |
| Technological Controls | Annex A 8.7 | Annex A 12.2.1 | Protection Against Malware |
| Technological Controls | Annex A 8.8 |
Annex A 12.6.1 Annex A 18.2.3 |
Management of Technical Vulnerabilities |
| Technological Controls | Annex A 8.9 | NEW | Configuration Management |
| Technological Controls | Annex A 8.10 | NEW | Information Deletion |
| Technological Controls | Annex A 8.11 | NEW | Data Masking |
| Technological Controls | Annex A 8.12 | NEW | Data Leakage Prevention |
| Technological Controls | Annex A 8.13 | Annex A 12.3.1 | Information Backup |
| Technological Controls | Annex A 8.14 | Annex A 17.2.1 | Redundancy of Information Processing Facilities |
| Technological Controls | Annex A 8.15 |
Annex A 12.4.1 Annex A 12.4.2 Annex A 12.4.3 |
Logging |
| Technological Controls | Annex A 8.16 | NEW | Monitoring Activities |
| Technological Controls | Annex A 8.17 | Annex A 12.4.4 | Clock Synchronization |
| Technological Controls | Annex A 8.18 | Annex A 9.4.4 | Use of Privileged Utility ProgramsAccess Rights |
| Technological Controls | Annex A 8.19 |
Annex A 12.5.1 Annex A 12.6.2 |
Installation of Software on Operational Systems |
| Technological Controls | Annex A 8.20 | Annex A 13.1.1 | Networks Security |
| Technological Controls | Annex A 8.21 | Annex A 13.1.2 | Security of Network Services |
| Technological Controls | Annex A 8.22 | Annex A 13.1.3 | Segregation of Networks |
| Technological Controls | Annex A 8.23 | NEW | Web filtering |
| Technological Controls | Annex A 8.24 |
Annex A 10.1.1 Annex A 10.1.2 |
Use of Cryptography |
| Technological Controls | Annex A 8.25 | Annex A 14.2.1 | Secure Development Life Cycle |
| Technological Controls | Annex A 8.26 |
Annex A 14.1.2 Annex A 14.1.3 |
Application Security Requirements |
| Technological Controls | Annex A 8.27 | Annex A 14.2.5 | Secure System Architecture and Engineering PrinciplesLearning From Information Security Incidents |
| Technological Controls | Annex A 8.28 | NEW | Secure Coding |
| Technological Controls | Annex A 8.29 |
Annex A 14.2.8 Annex A 14.2.9 |
Security Testing in Development and Acceptance |
| Technological Controls | Annex A 8.30 | Annex A 14.2.7 | Outsourced Development |
| Technological Controls | Annex A 8.31 |
Annex A 12.1.4 Annex A 14.2.6 |
Separation of Development, Test and Production Environments |
| Technological Controls | Annex A 8.32 |
Annex A 12.1.2 Annex A 14.2.2 Annex A 14.2.3 Annex A 14.2.4 |
Change Management |
| Technological Controls | Annex A 8.33 | Annex A 14.3.1 | Test Information |
| Technological Controls | Annex A 8.34 | Annex A 12.7.1 | Protection of Information Systems During Audit Testing |
Why choose ISMS.online for Annex A 5.34?
Our cloud platform gives you a framework of information security controls for your ISMS. With ISMS.online you can:
- Work through your ISMS step by step against the requirements of ISO 27001:2022.
- Get a head start from the moment you log on: much of the hard work is done for you, so you fill in the blanks.
- Embed, expand and scale your compliance without the mess of spreadsheets.
- Build the resilience and confidence to grow securely.
- Work towards ISO 27001 certification; certificates are issued by accredited certification bodies.
To see how ISMS.online can help with your ISO 27001 ISMS, book a demo.
Frequently asked questions about Annex A 5.34
Is ISO 27001 the same as GDPR compliance?
No. UK GDPR is law that applies to organisations processing personal data within its scope, while ISO 27001 is a voluntary standard for an information security management system. An ISO 27001 certificate relates to the ISMS within its certified scope and is not a finding of UK GDPR compliance. UK GDPR also covers matters ISO 27001 does not, such as the lawful basis for processing (Article 6) and people’s right of access to their data (Article 15).
Does Annex A 5.34 apply if we only hold staff data?
Employee records such as payroll and bank details are PII, so most organisations with staff will have privacy requirements to identify under this control. Any decision to include or exclude an Annex A control is recorded, with a justification, in the Statement of Applicability (ISO 27001:2022 clause 6.1.3 d).

NHS Professionals achieves ISO 27001 certification and improves their infosec management
Facing a tight six-month deadline and multiple existing frameworks to integrate, NHS Professionals needed a platform that could incorporate ISO 27001 without duplicating policies or adding risk to their already complex compliance landscape.
Xergy tool Proteus generates growth through ISO 27001 compliance using ISMS.online
As a start-up building software for highly regulated engineering sectors, Xergy needed ISO 27001 to generate growth through trust — and a proven external partner to handle the rigorous requirements without diverting the dev team.
How MAAS Aviation Built a Robust and Sustainable ISO 27001-Compliant ISMS
MAAS Aviation required strong technical foundations to support ISO 27001 alignment, and a platform to centralise compliance management.
How Blue Services Achieved Triple ISO Certification Success
Blue Services needed external support to guide them through ISO 27001, ISO 9001 and ISO 14001 implementation and best practices, and a platform to centralise their overall compliance management.
How Evolution Funding Cruised to ISO 27001 Certification Success
Achieving ISO 27001 certification was a core objective for Evolution Funding. The team needed a centralised platform with which they could implement the ISO 27001 standard and work through the compliance process.
How 4way Consulting Paved the Road to ISO 27001 Success
Handling sensitive client data across multiple standards, 4way needed a cost and time-efficient way to pursue ISO 27001 – without building an ISMS from scratch or relying on expensive external consultants.